

SAML SSO is available from the Advanced pack. Setting it up requires a role
with Security: Can edit in its company settings permissions, and admin
access to your identity provider.
Set up SAML SSO
1
Turn on SAML SSO in Qobra
In Settings > Security, turn on 1 SAML SSO. The Configure SAML
SSO dialog opens. Later, reopen it with 2 Edit SAML SSO configuration.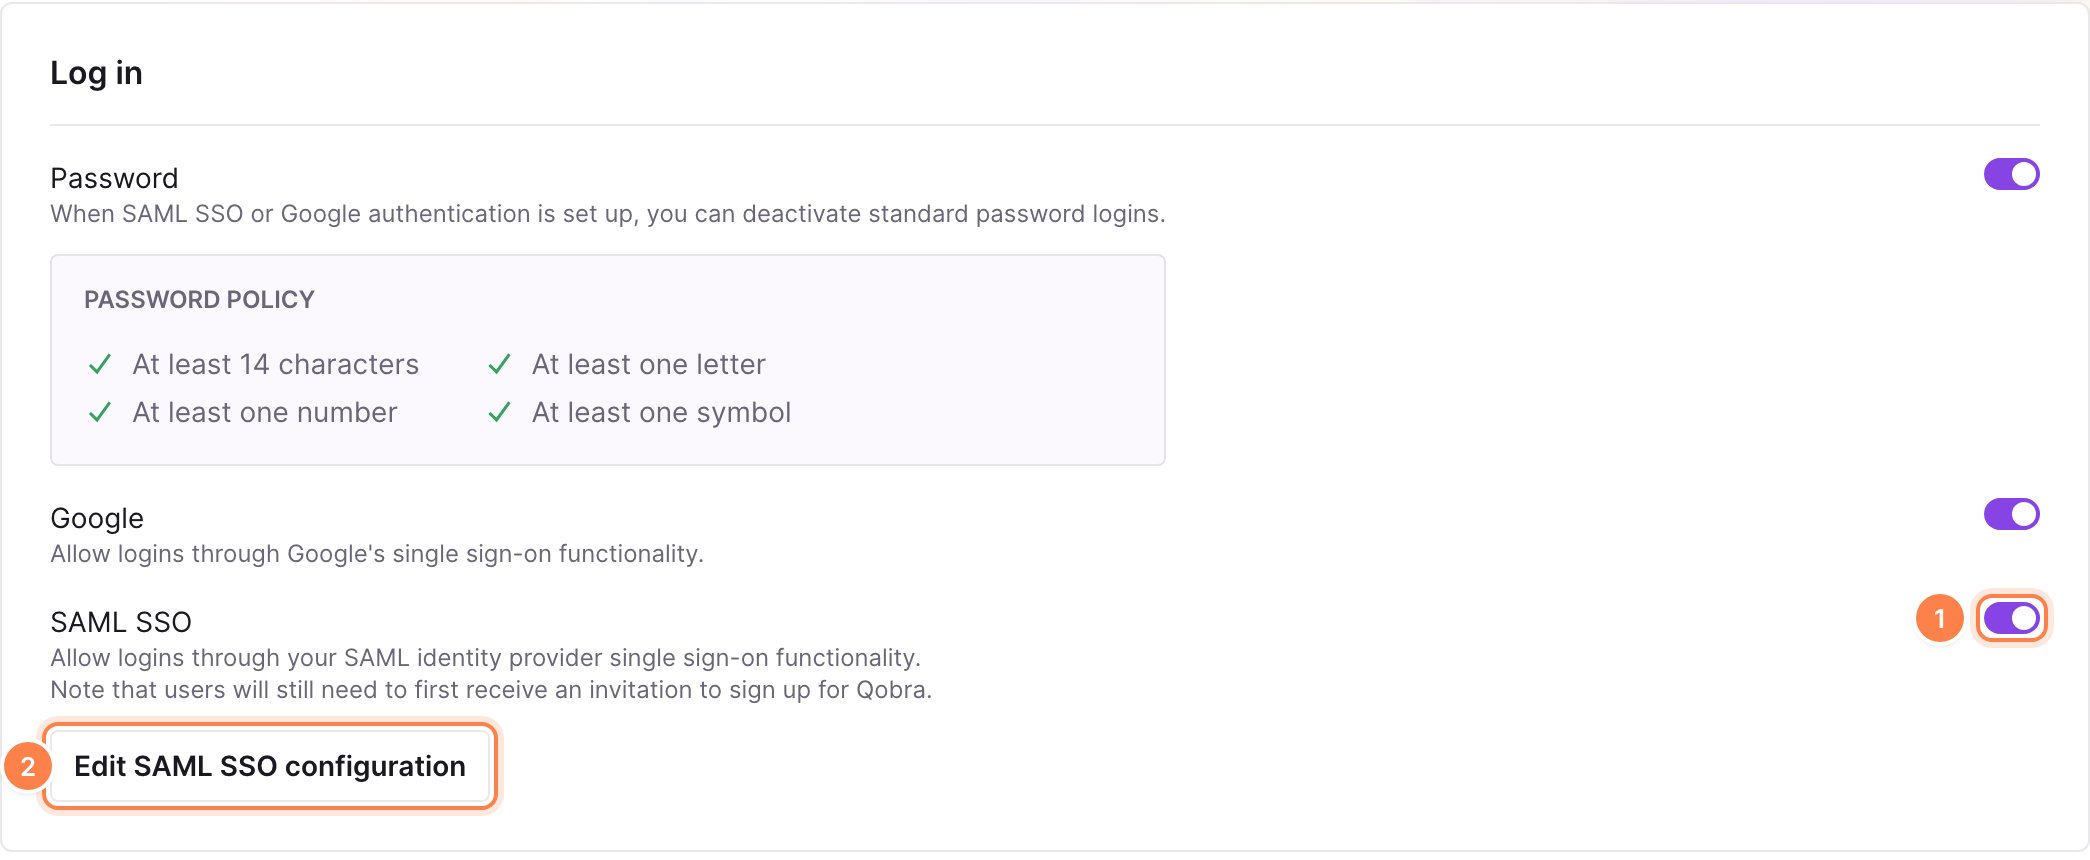
2
Copy the Qobra values into your identity provider
In your identity provider, create a SAML 2.0 application for Qobra and
paste the two values of the dialog, with their copy buttons: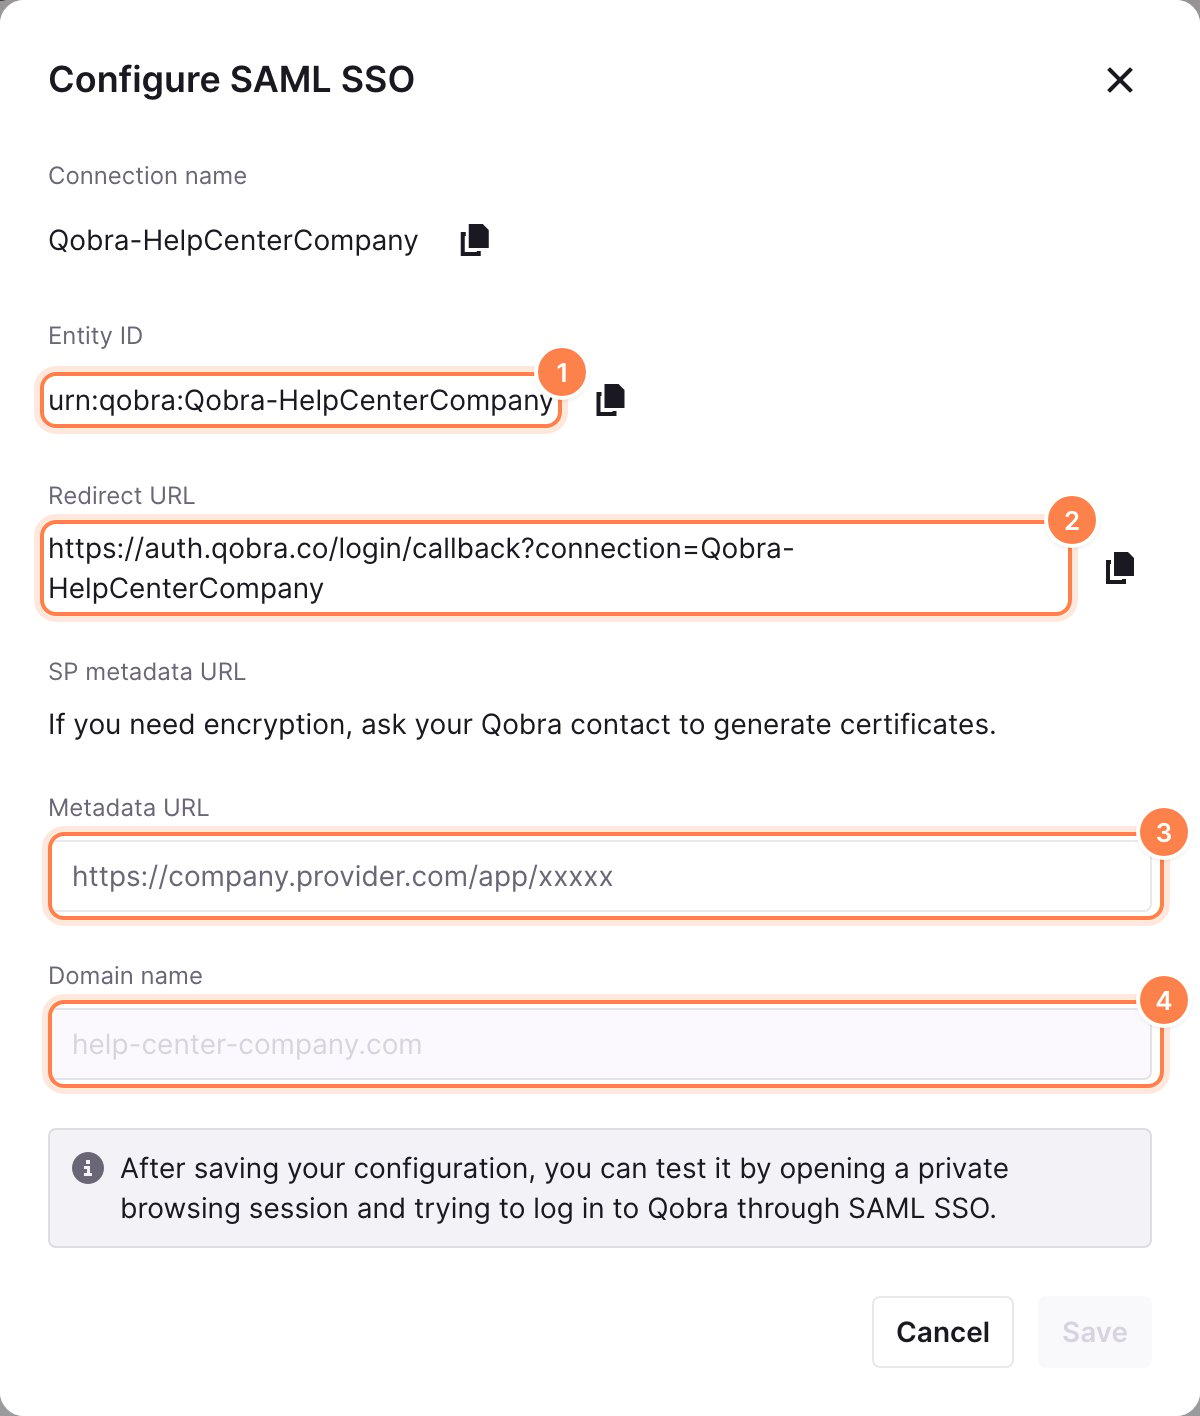
- 1 Entity ID: the identifier of your Qobra account, also called Audience URI or Identifier.
- 2 Redirect URL: where your identity provider sends users back once they are authenticated, also called Single sign-on URL, Reply URL, ACS URL or Callback URL.
3
Paste your identity provider's metadata URL in Qobra
Back in Qobra, fill in:
- 3 Metadata URL: the public URL of your identity provider’s SAML metadata, an XML document with its endpoints and signing certificate.
- 4 Domain name: the domain of your users’ work emails. It is filled in with the domain of your own email. To add another domain, after a merger or a rebranding for example, contact support@qobra.co: for security, you can’t add one yourself.
4
Test the connection
Open a private browsing window, go to
https://app.qobra.co/auth and click
Log in with SSO. Enter an email of your domain: you should go through
your identity provider and land in Qobra. Keep your current session open
until the test succeeds.What the metadata looks like
The metadata URL must return an XML document like this one:Identity provider tutorials
Step-by-step setups for the identity providers our customers use the most. To see another one here, write to support@qobra.co.Okta
Okta
-
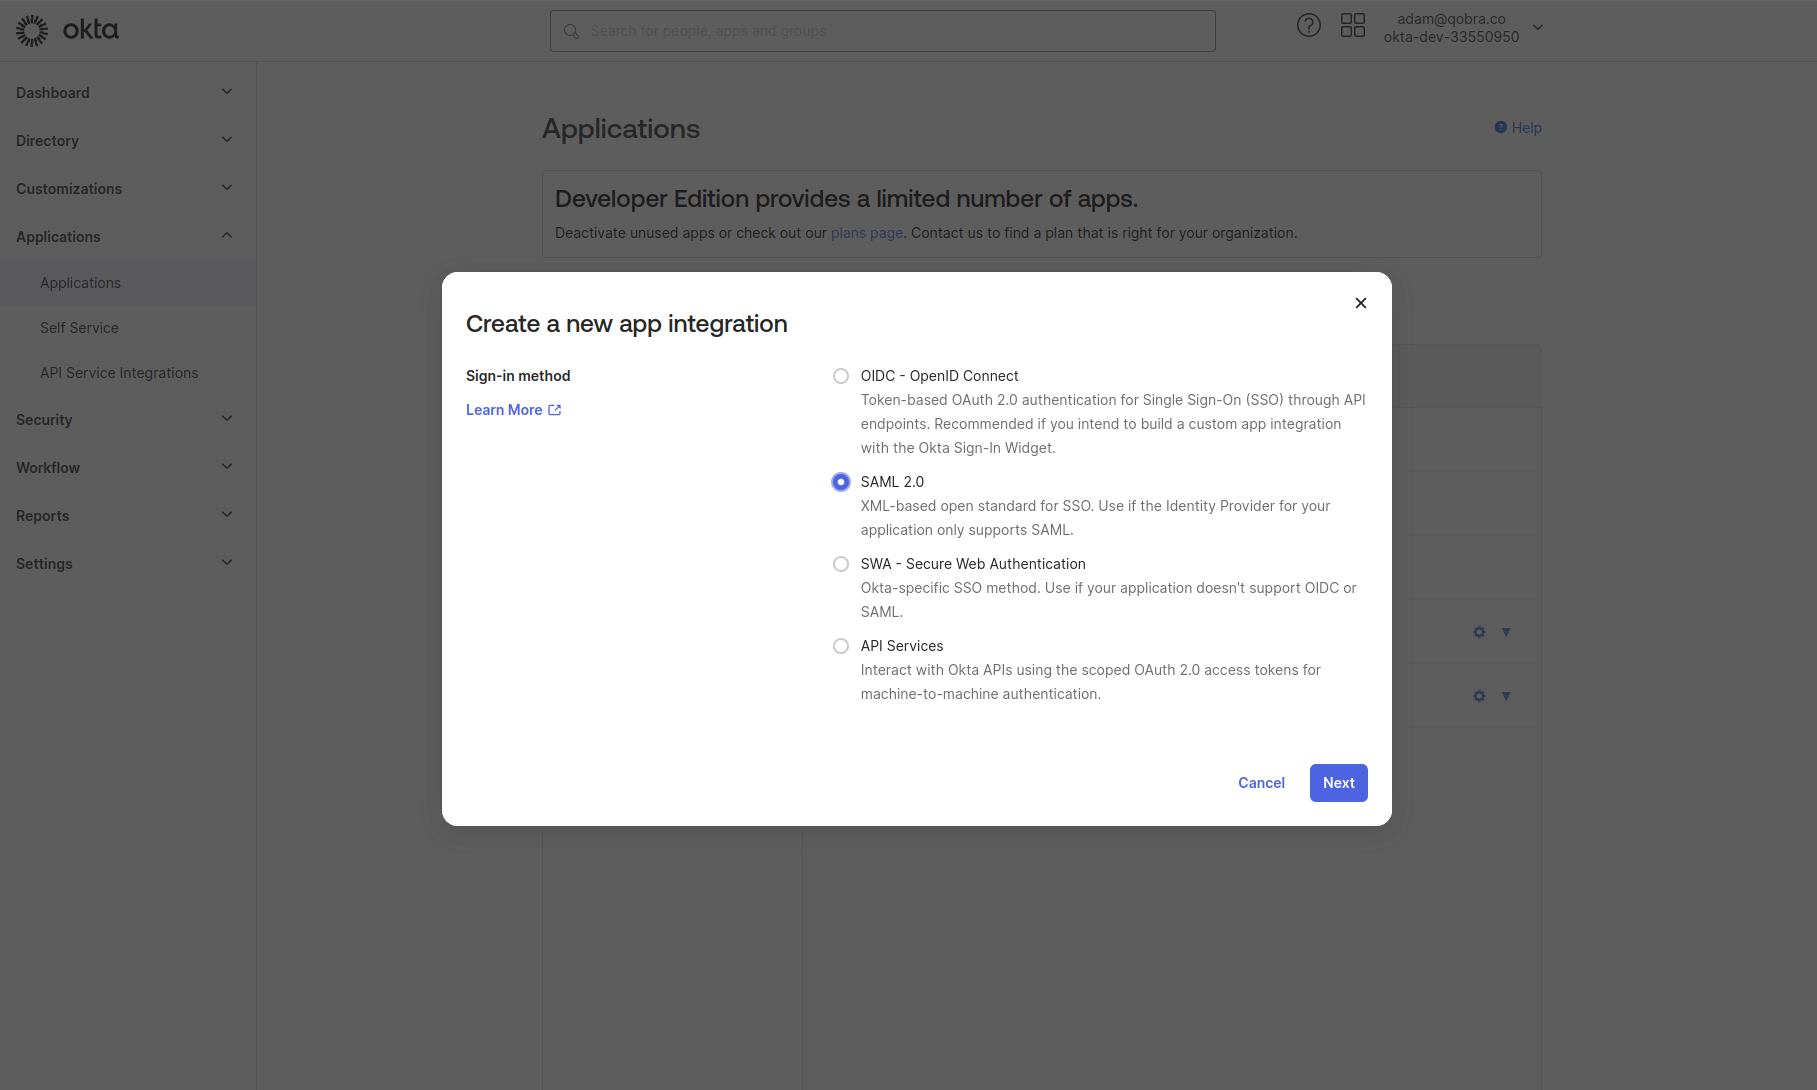
In the Okta Admin Console, go to Applications and click Create App Integration. Select SAML 2.0.
-
Fill in the general settings: name the app
Qobraand add its logo if you like.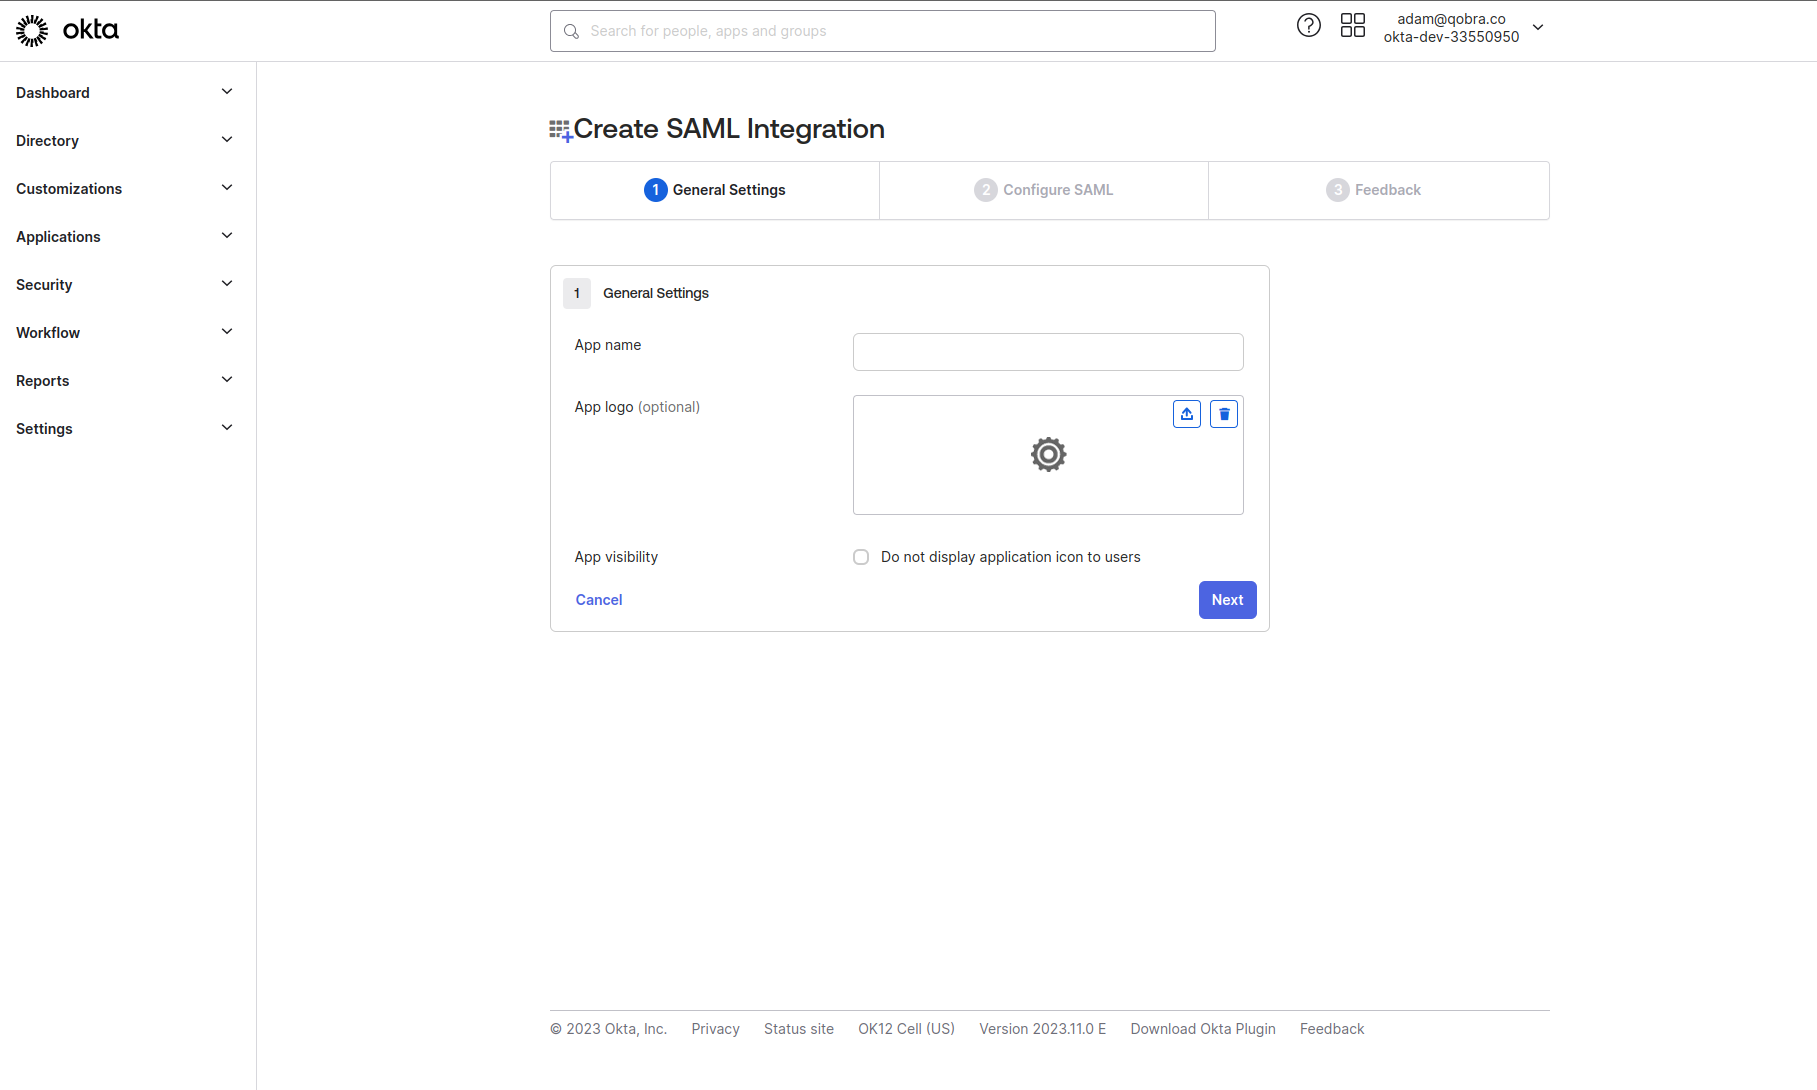
-
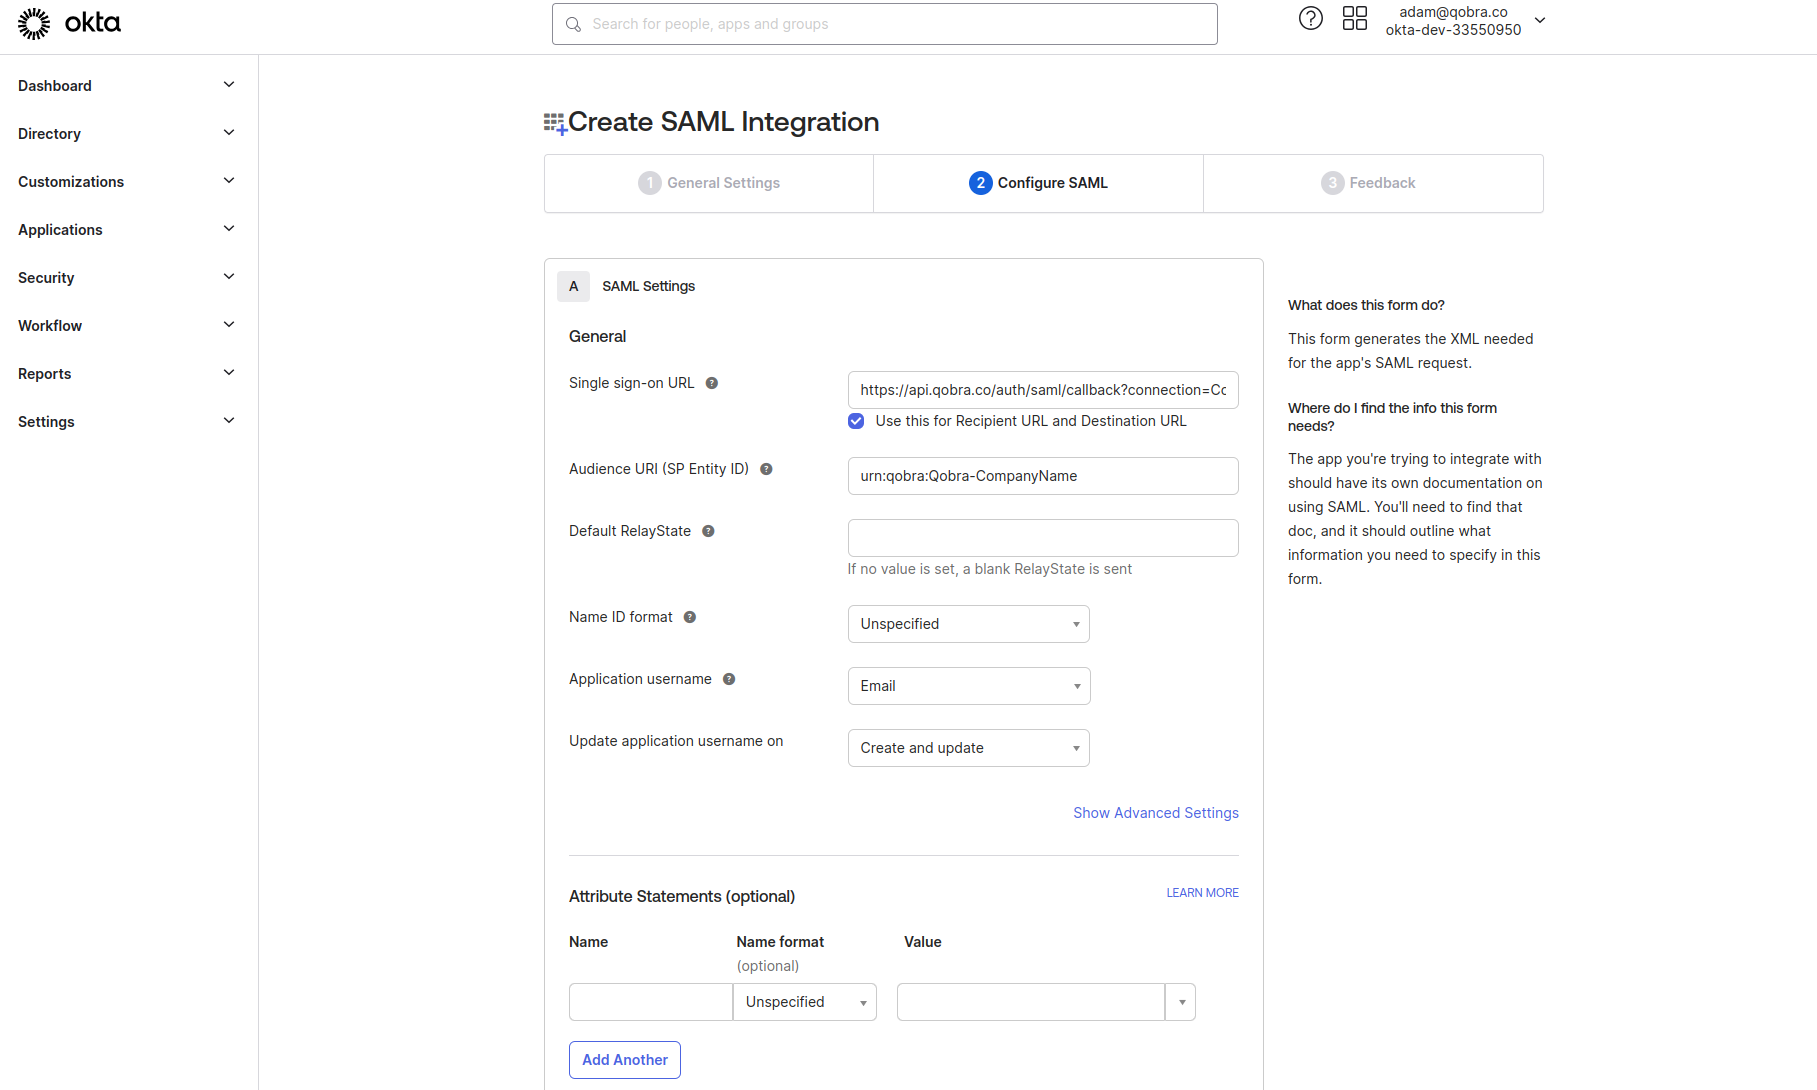
Fill in the SAML settings as shown below: Single sign-on URL is the Qobra Redirect URL and Audience URI is the Qobra Entity ID. Your IT team may require advanced settings of its own.
-
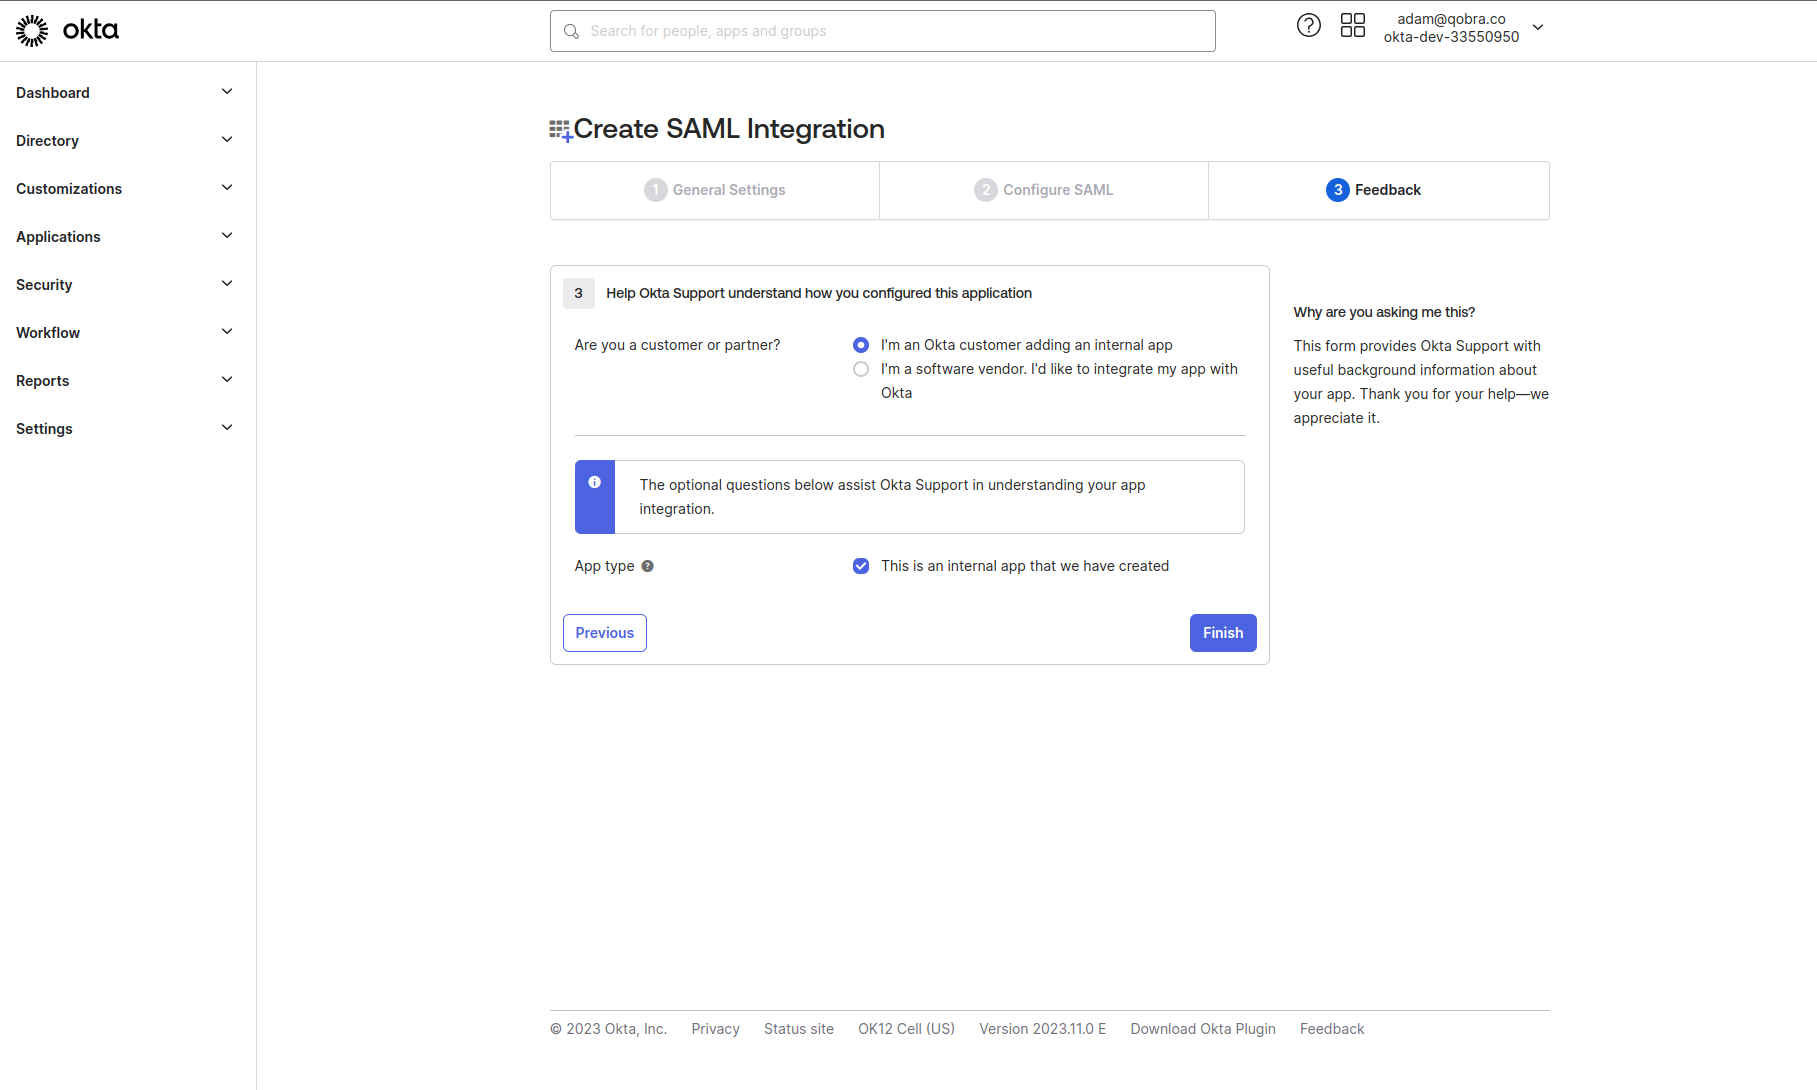
Finish the setup.
-
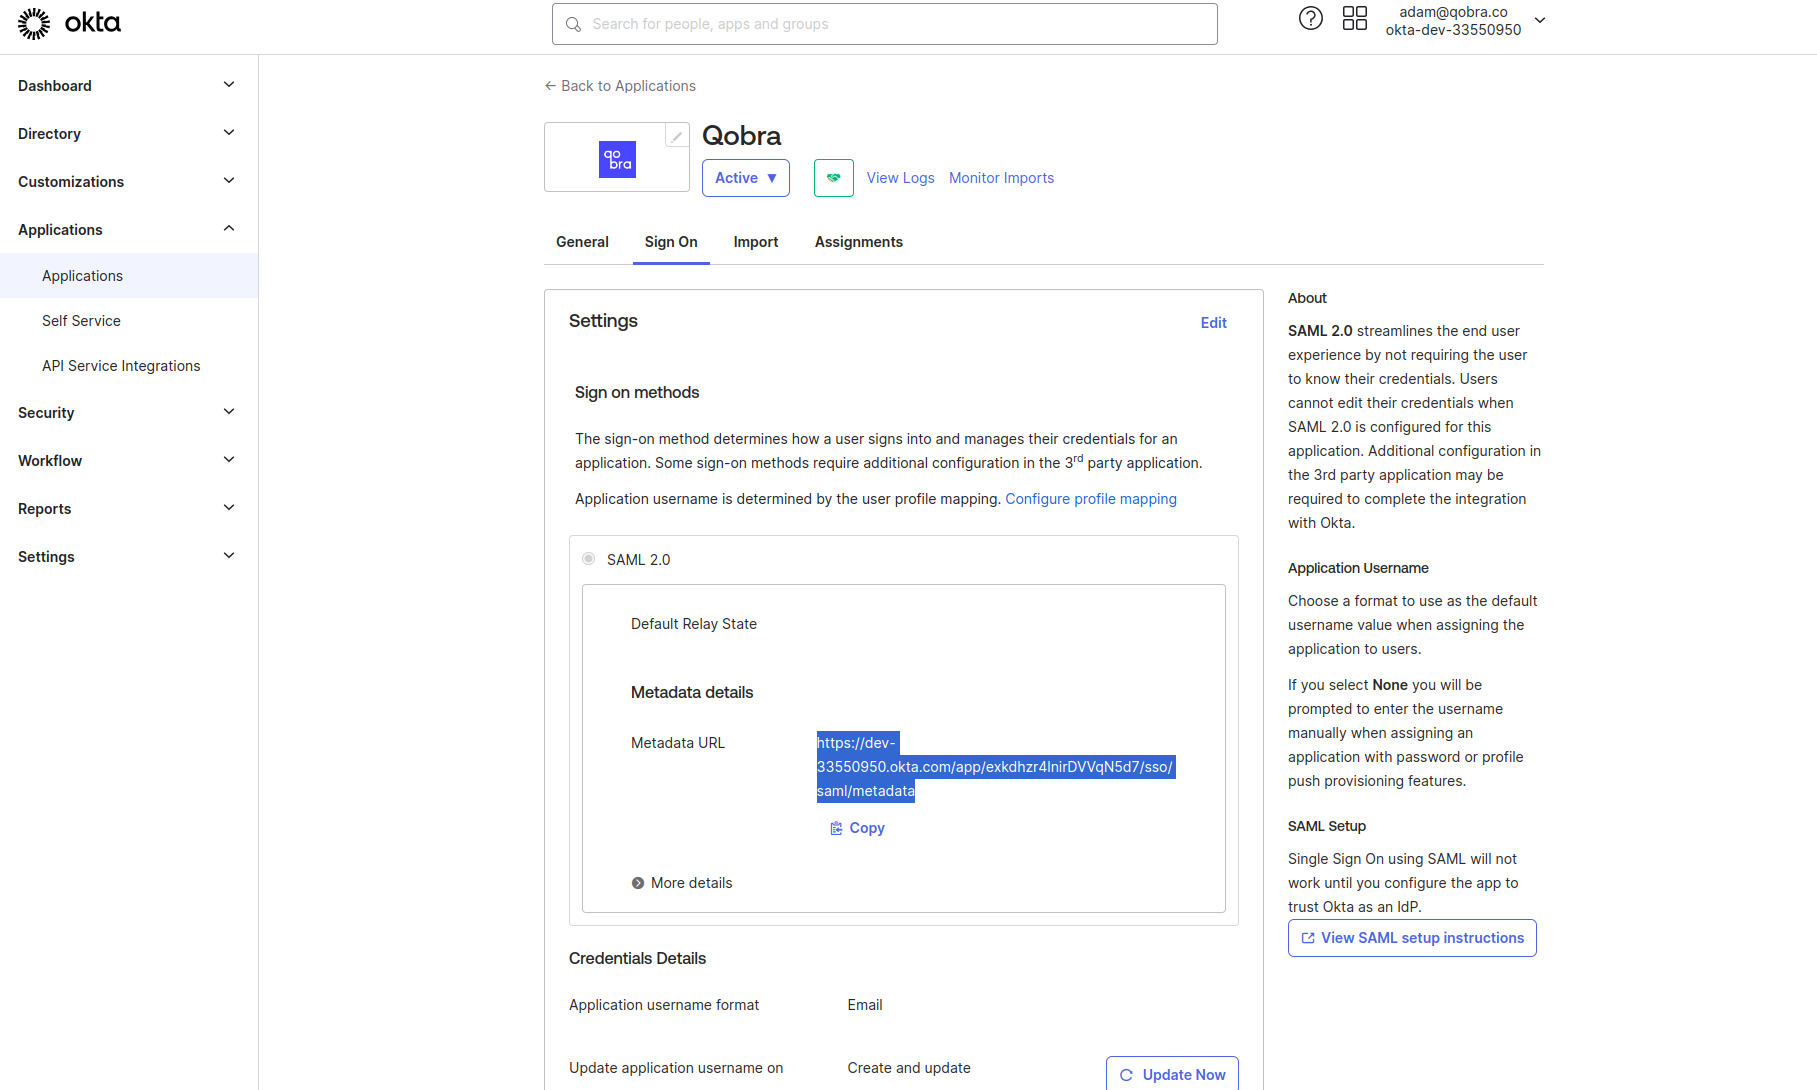
Copy the metadata URL of the app and paste it in the Qobra Metadata URL field.
- Assign the people or groups who sign in to Qobra to the app.
Microsoft Entra ID (Azure AD)
Microsoft Entra ID (Azure AD)
-
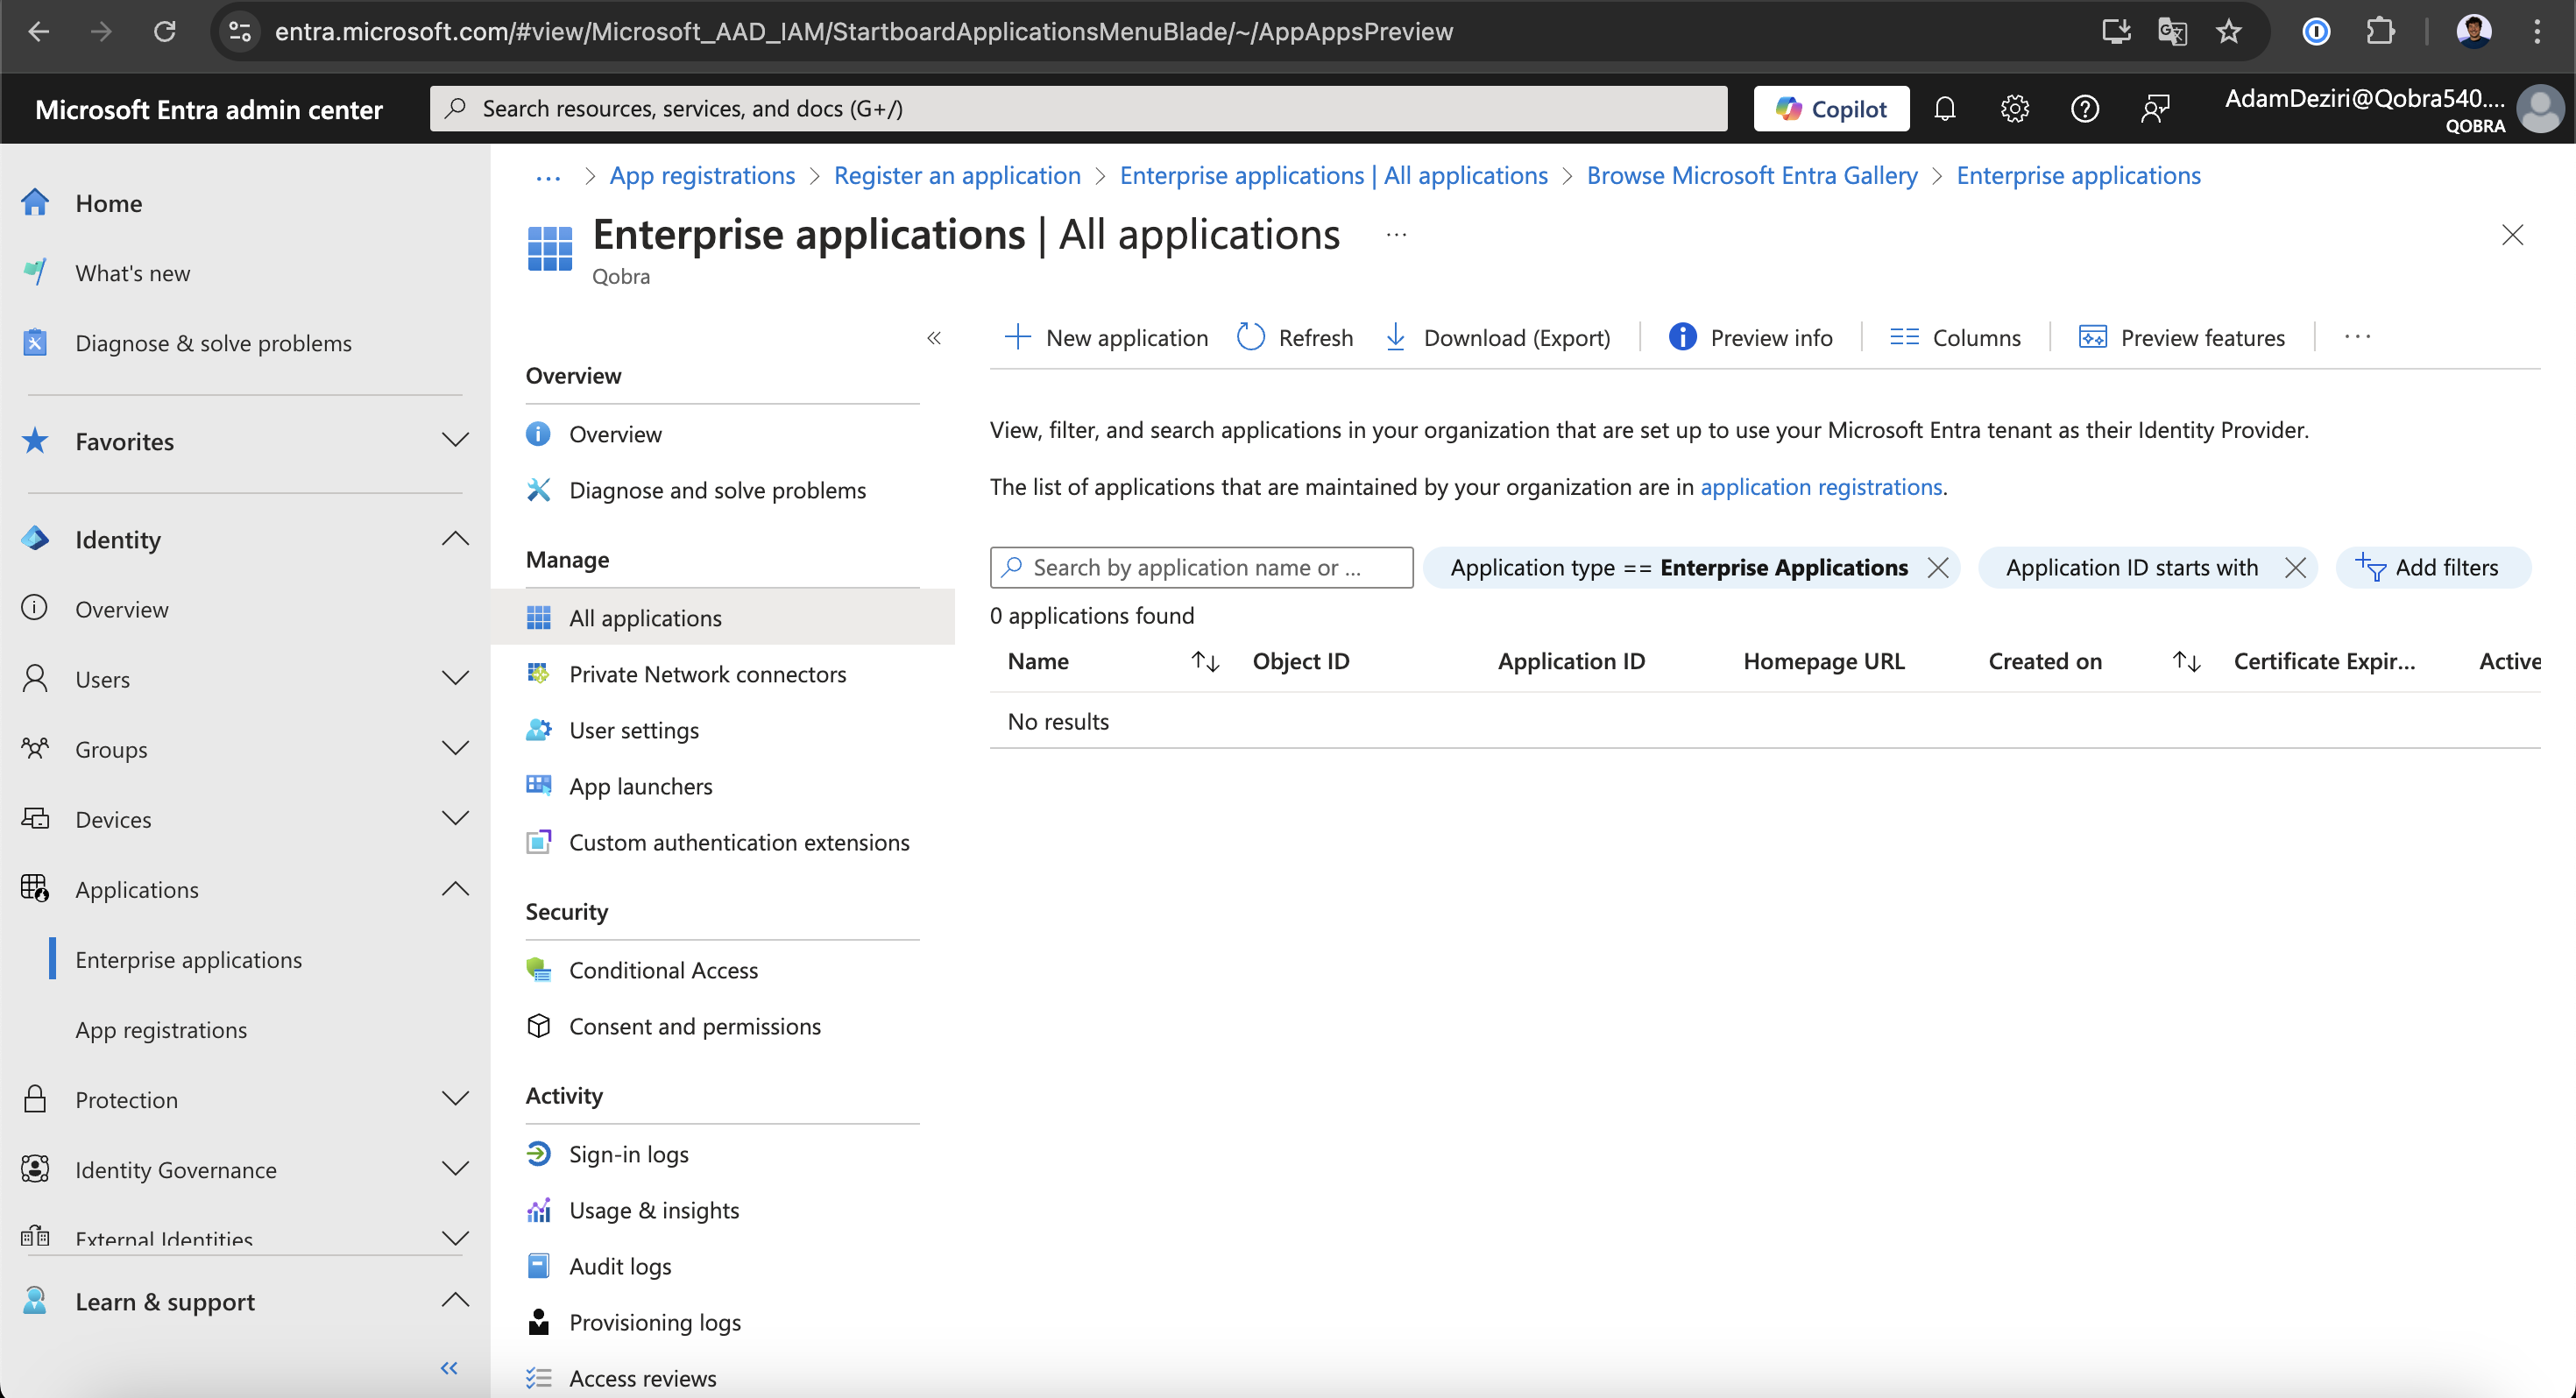
Go to Enterprise applications and click New application.
-
Select the Microsoft Entra SAML Toolkit application, name it
Qobraand click Create.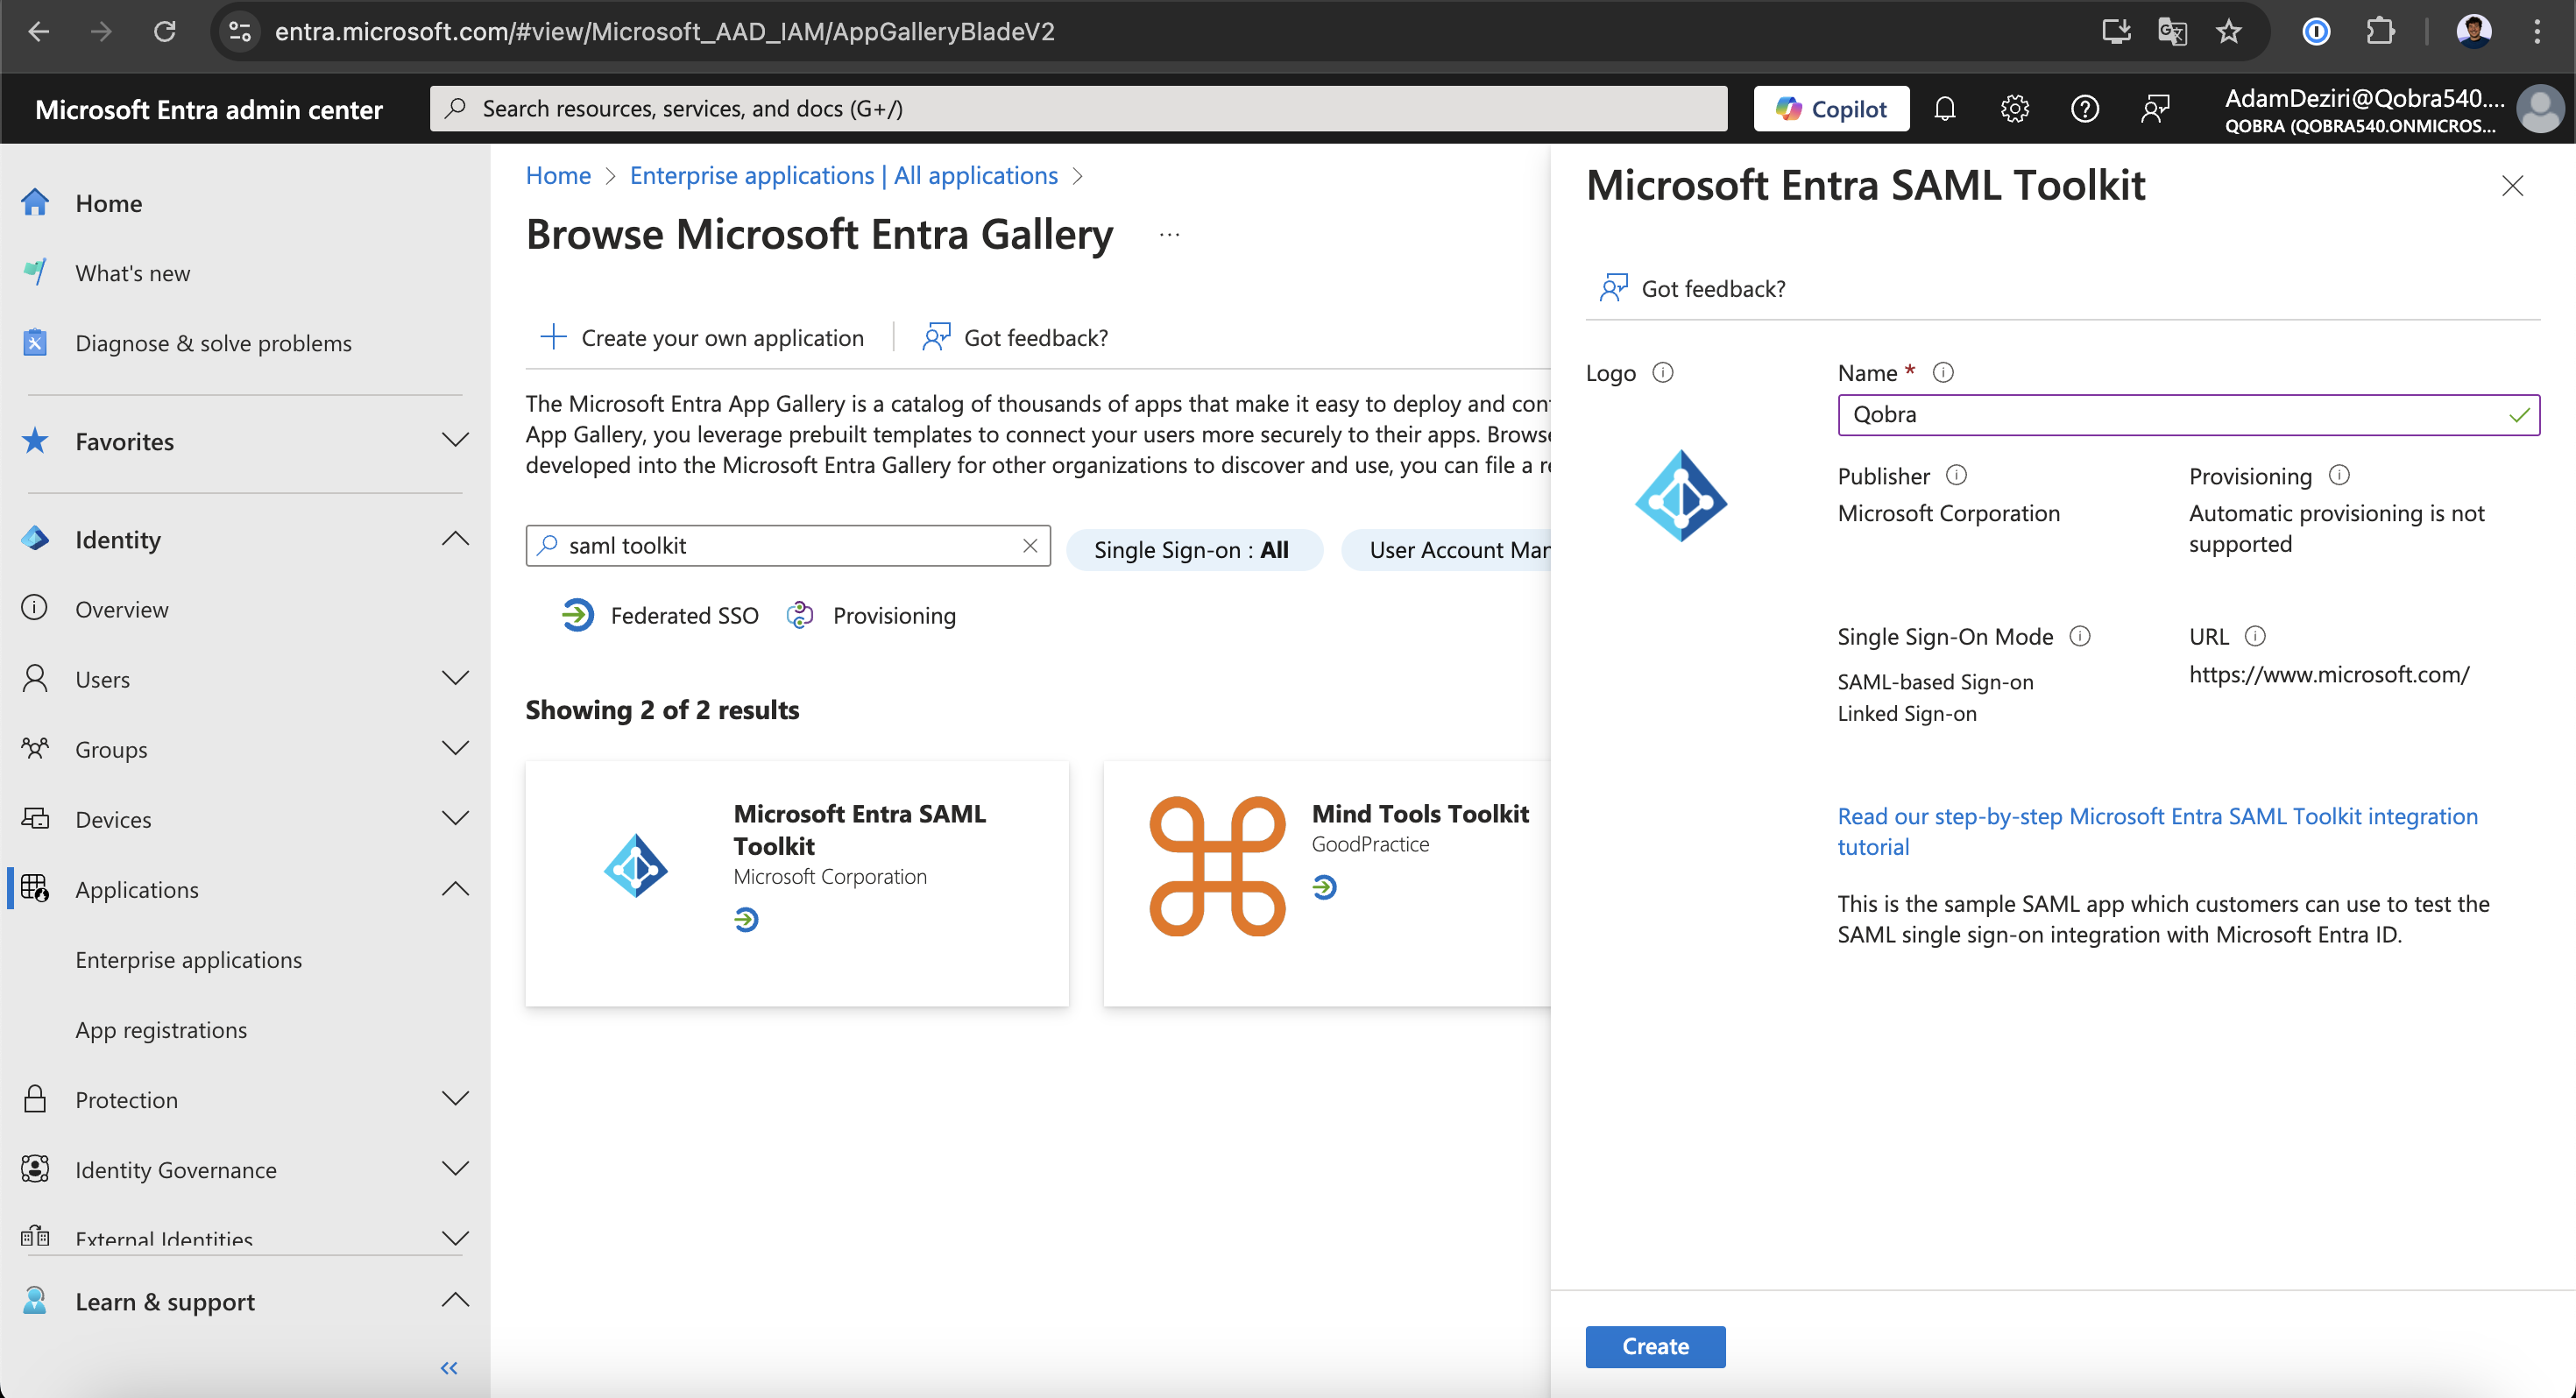
-
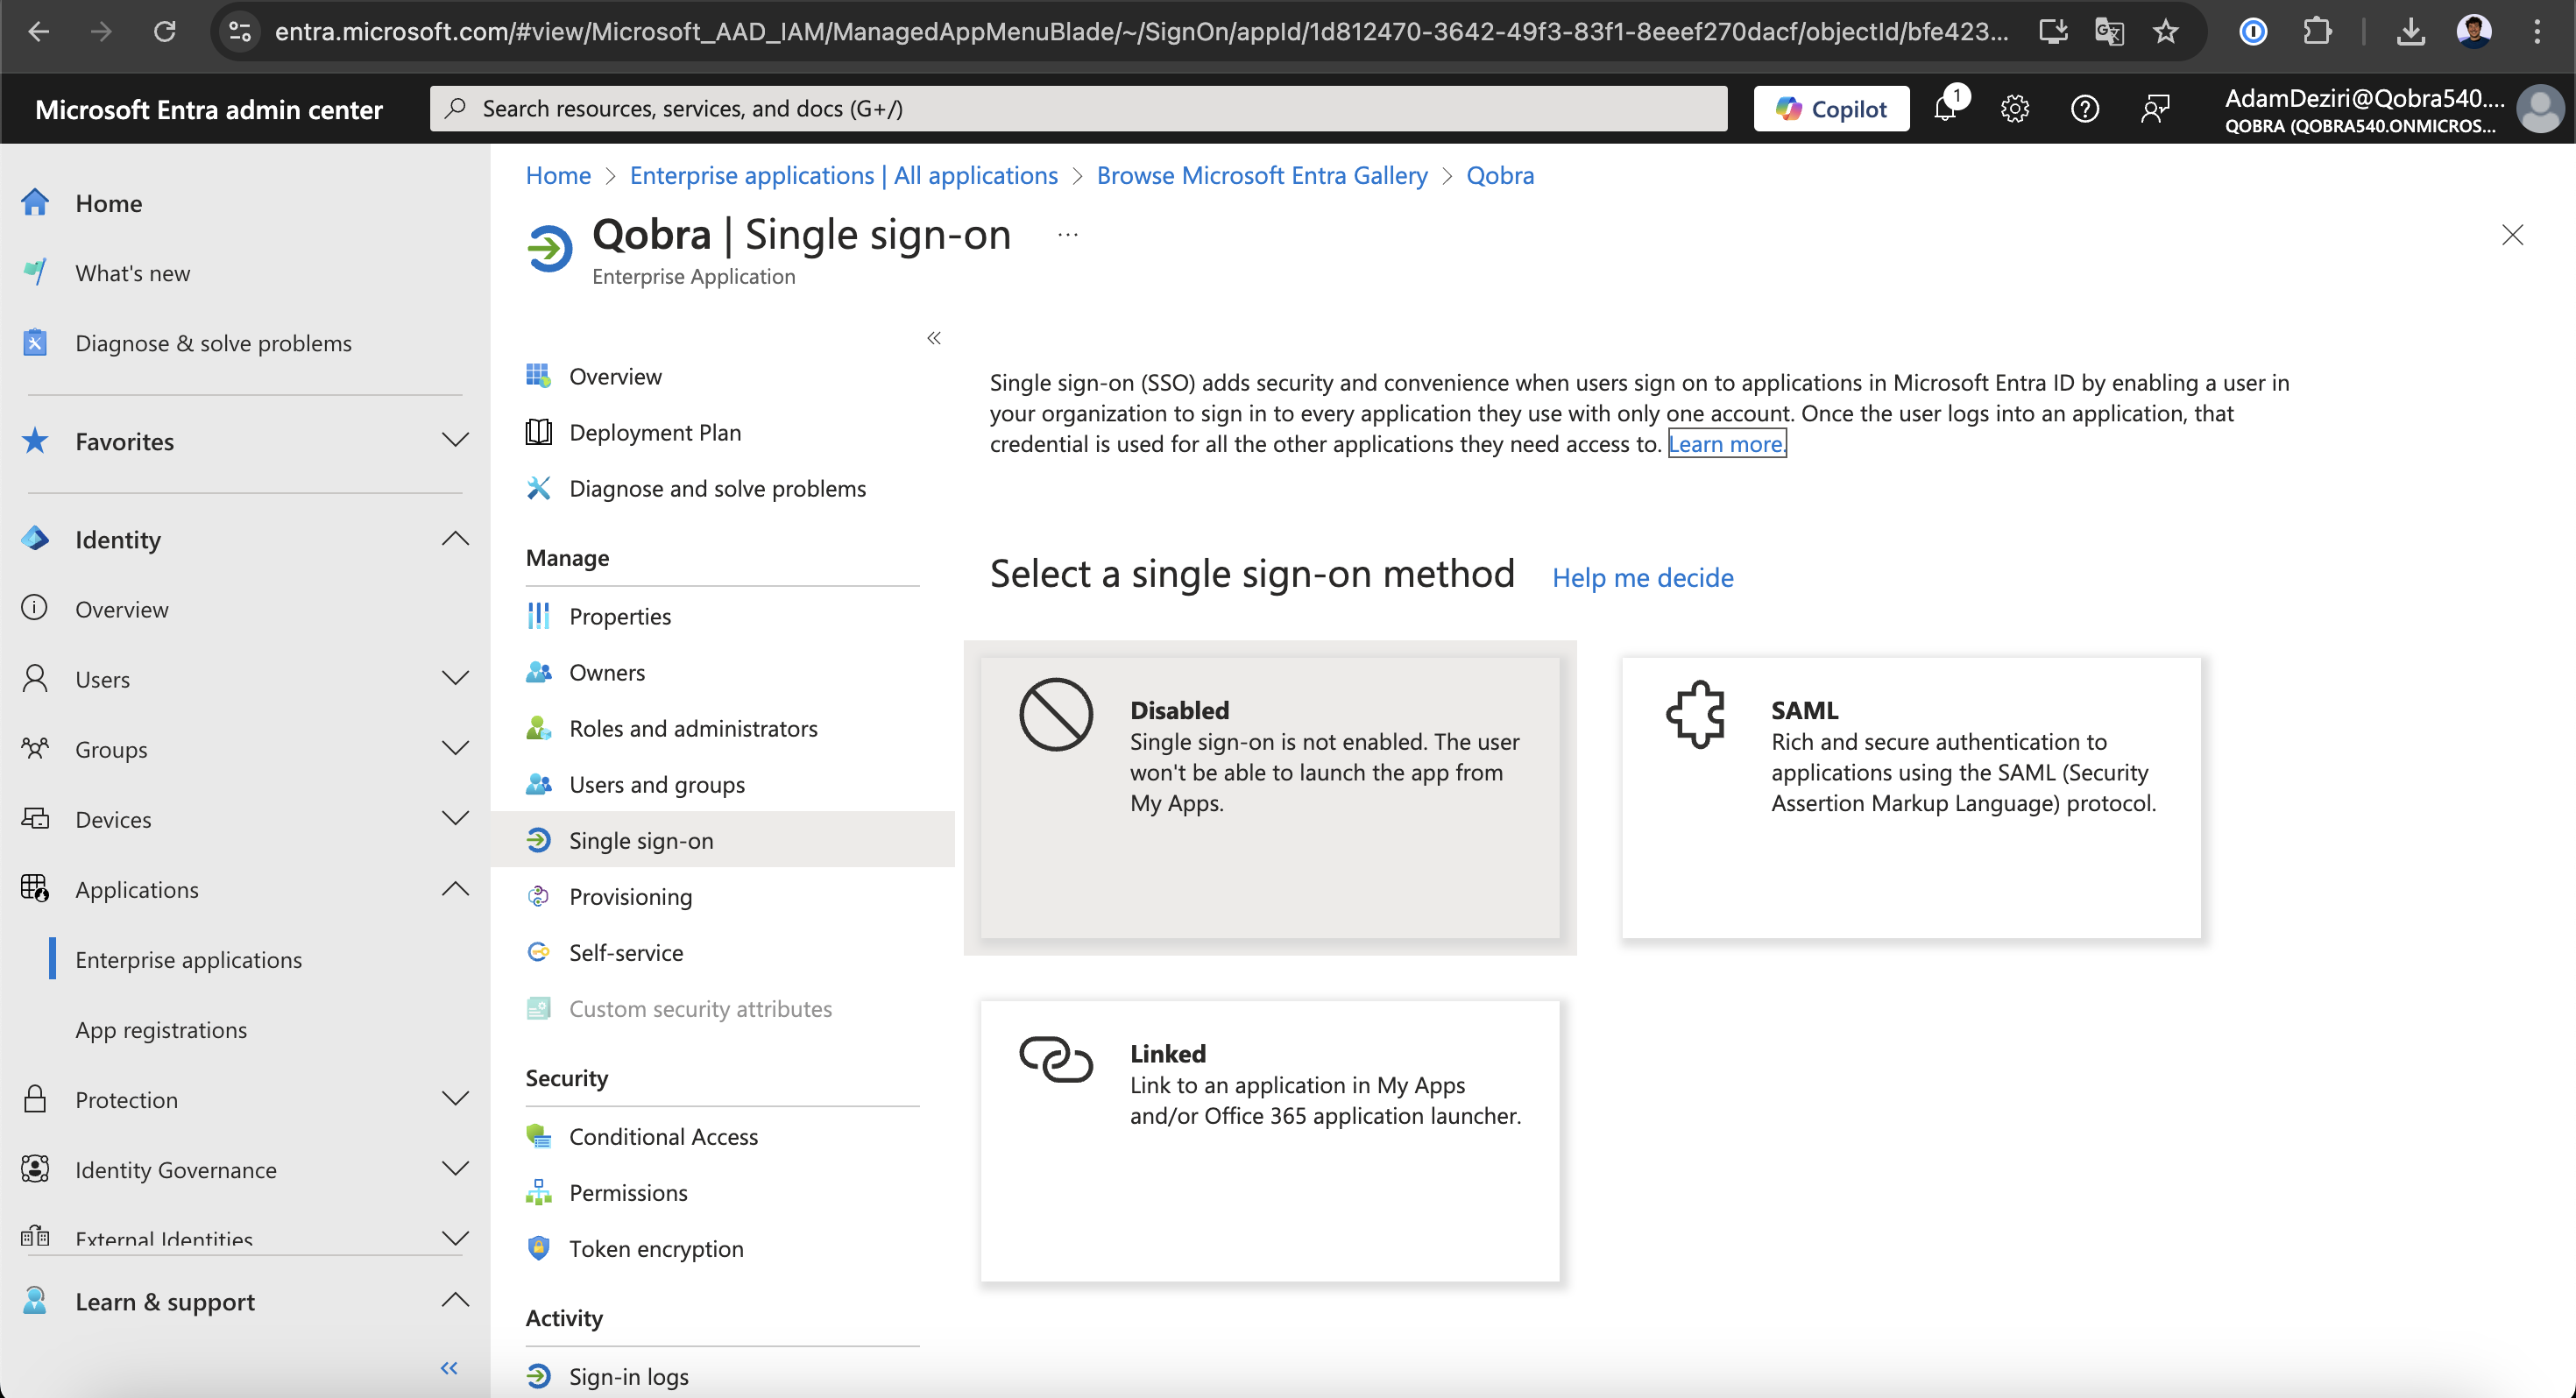
In the new application, open Single sign-on and select SAML.
-
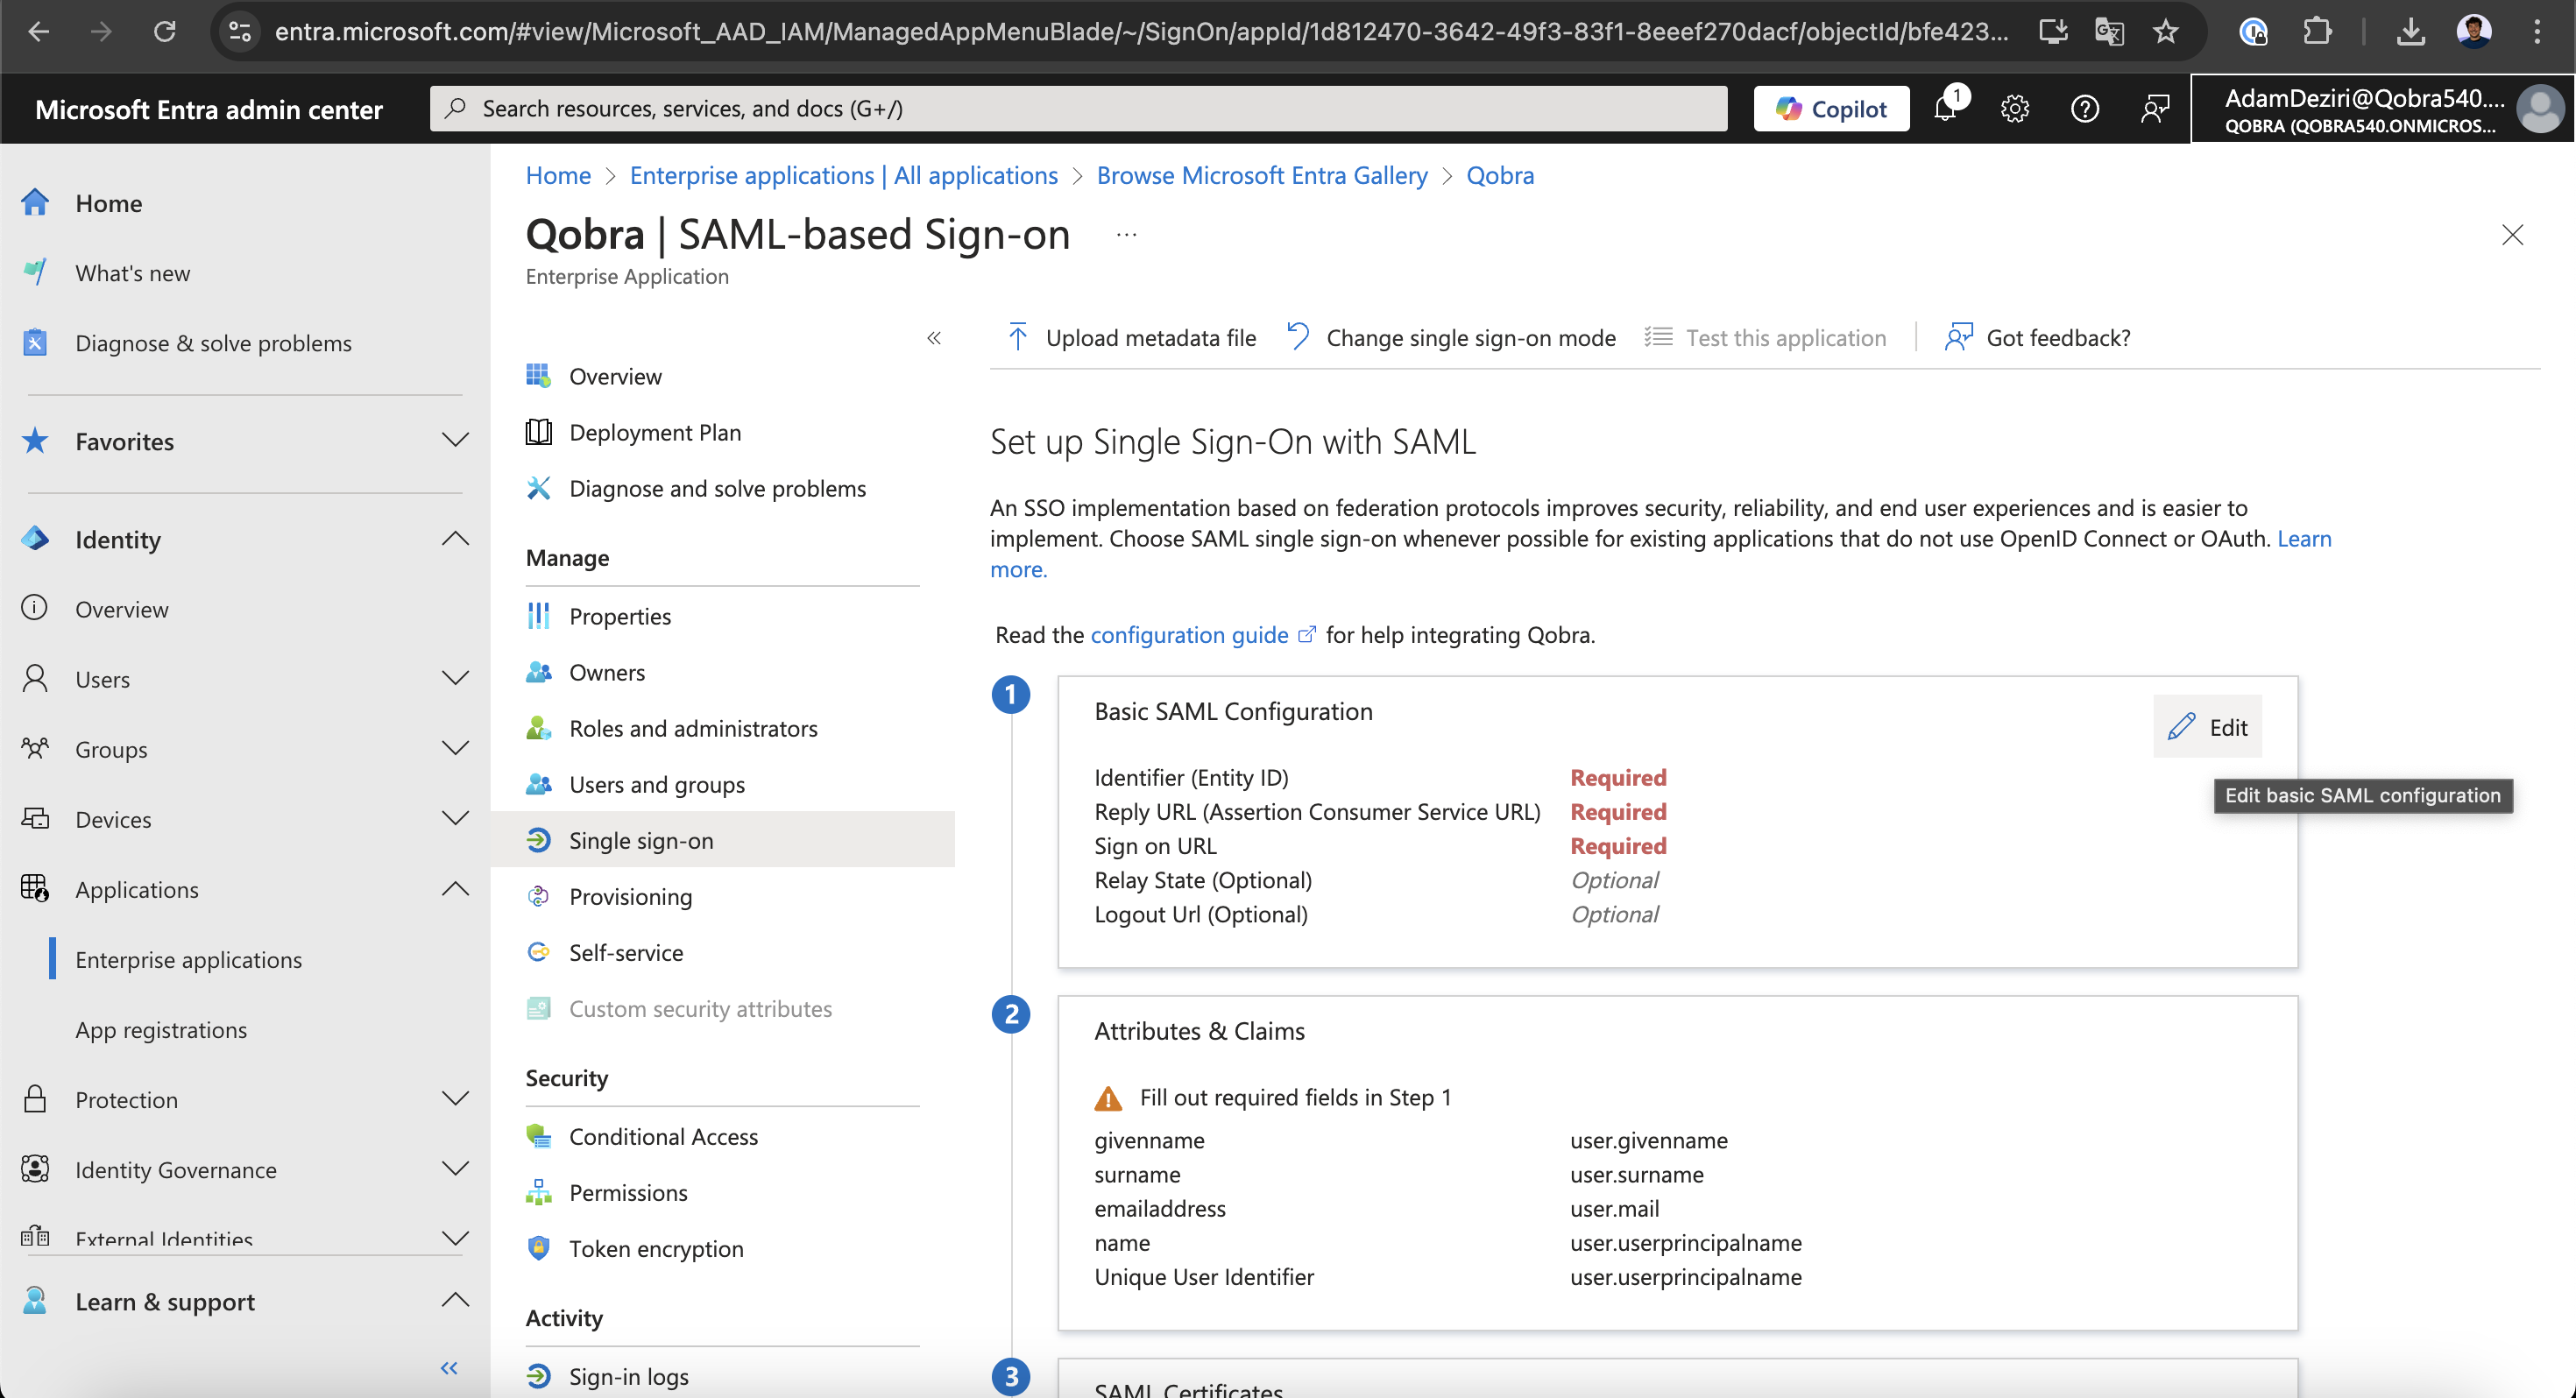
Click Edit to fill in the SAML data.
-
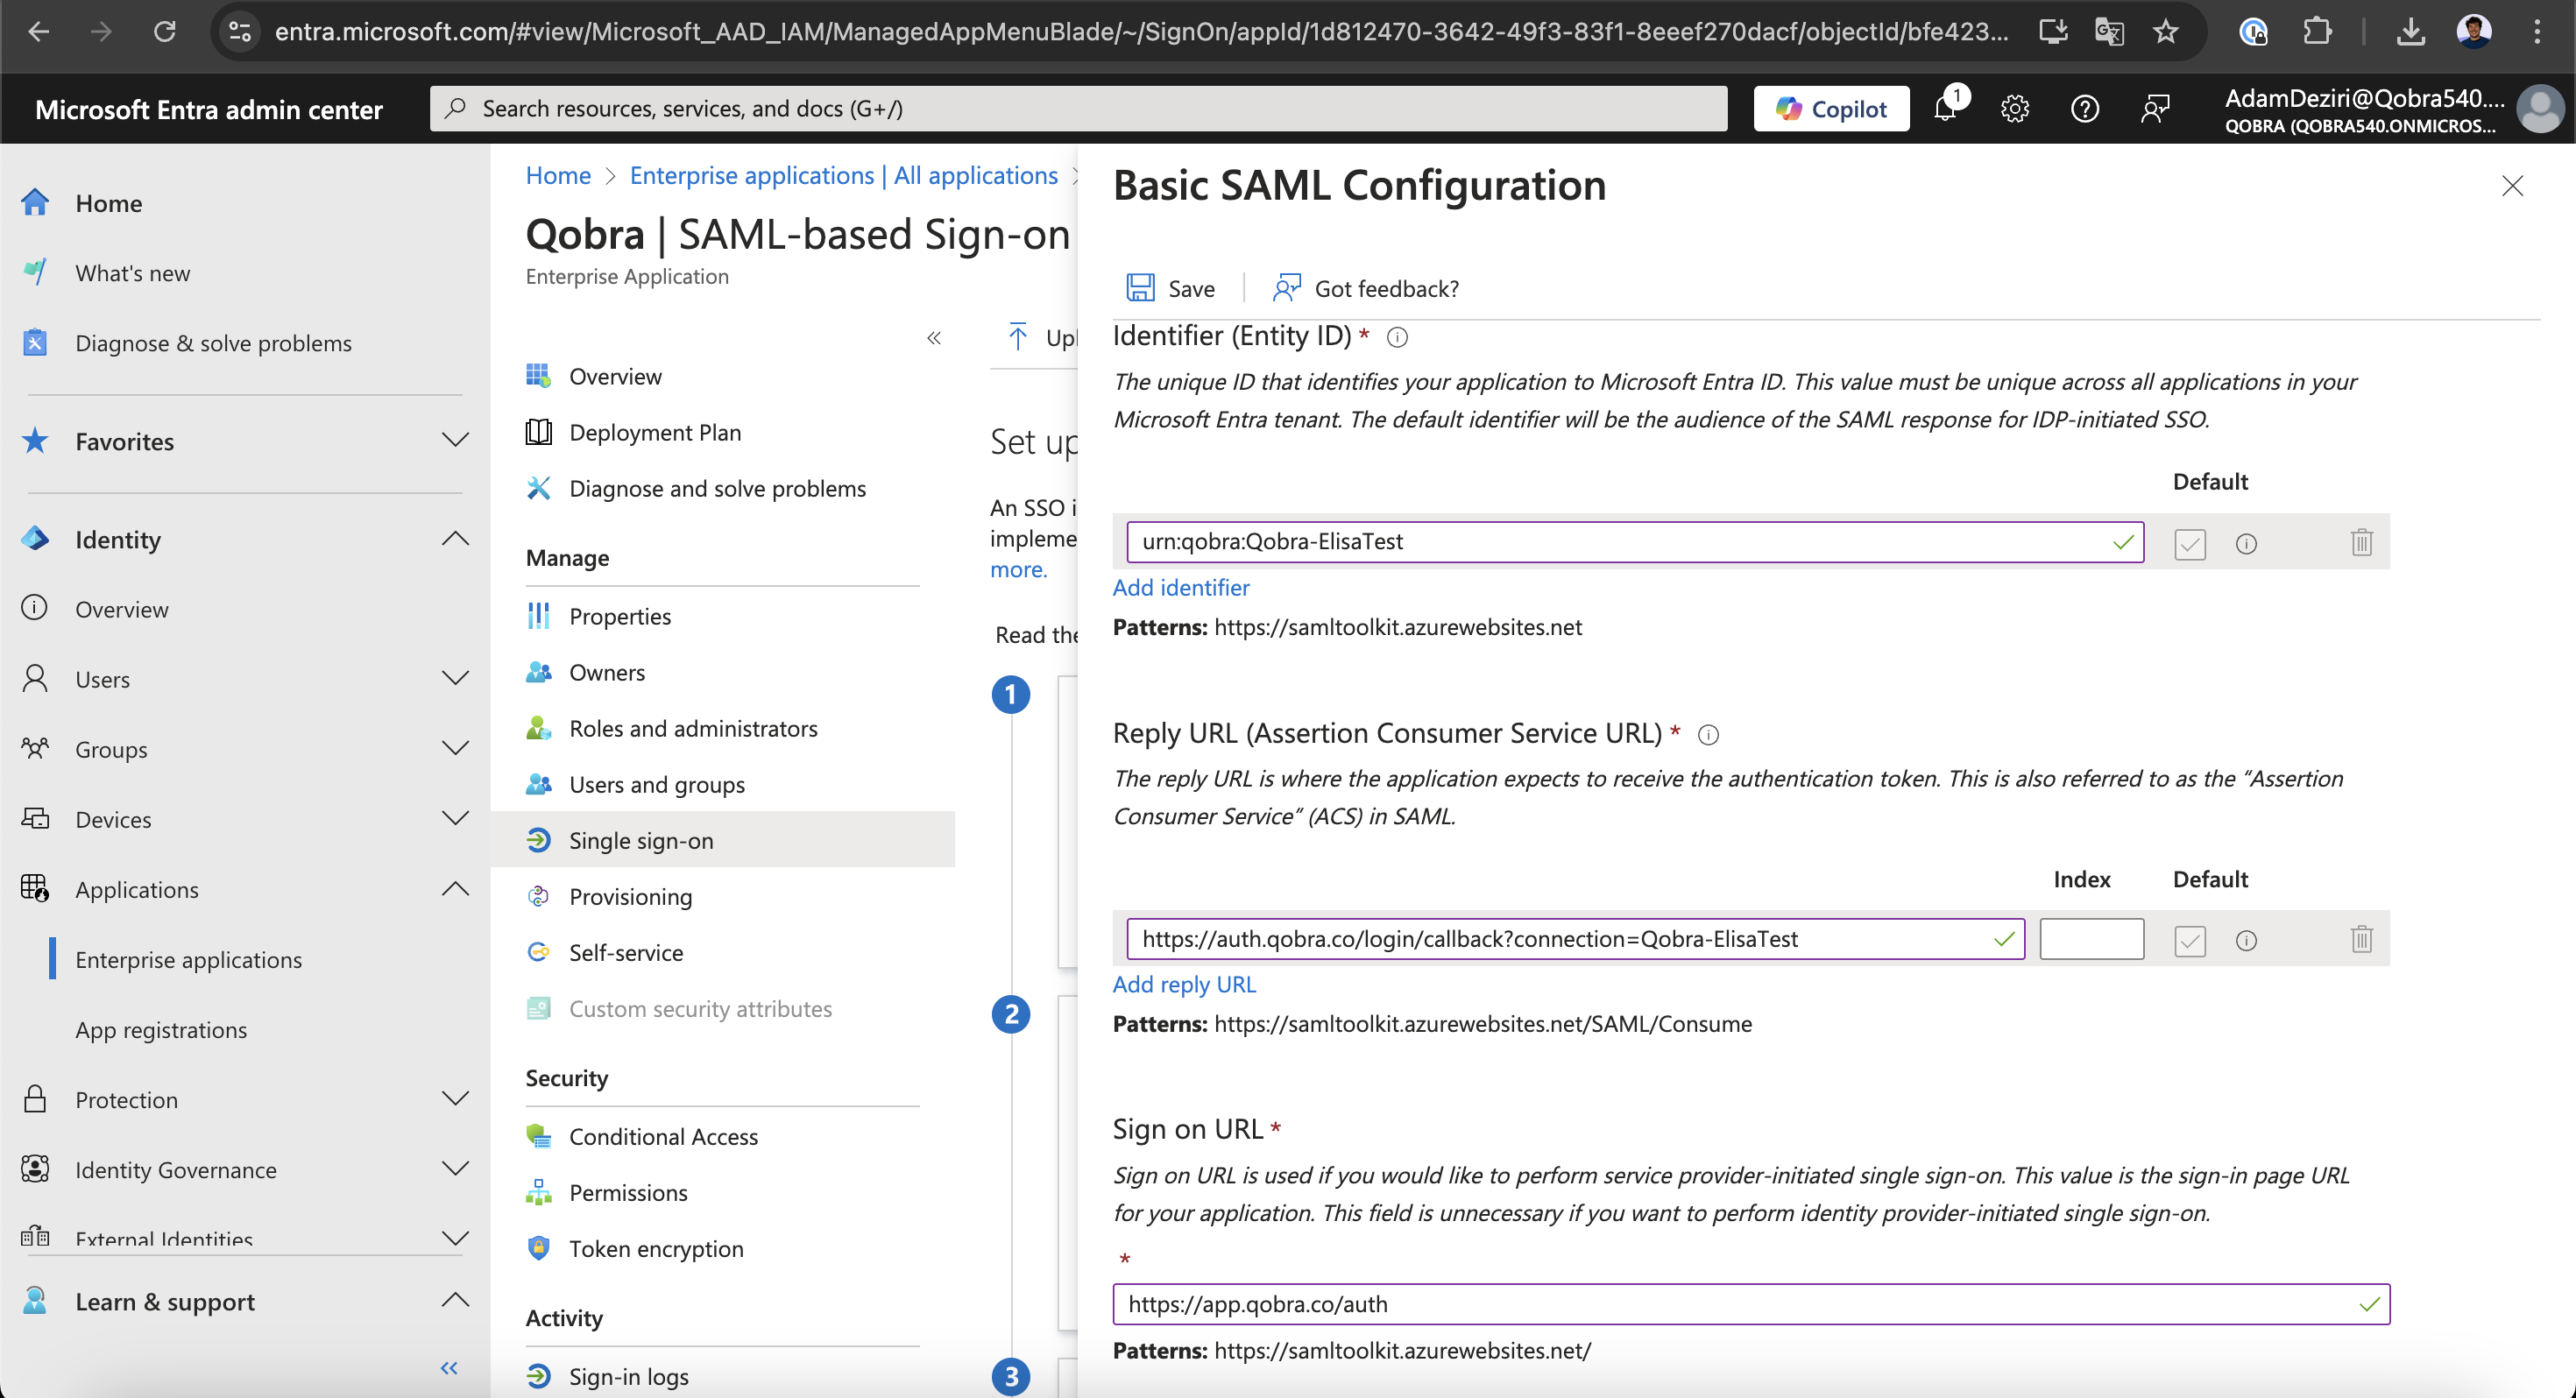
Fill in the three fields with the values of the Qobra Configure SAML SSO dialog, then click Save:
- Identifier (Entity ID): the Qobra Entity ID;
- Reply URL: the Qobra Redirect URL;
- Sign on URL:
https://app.qobra.co/auth.
-
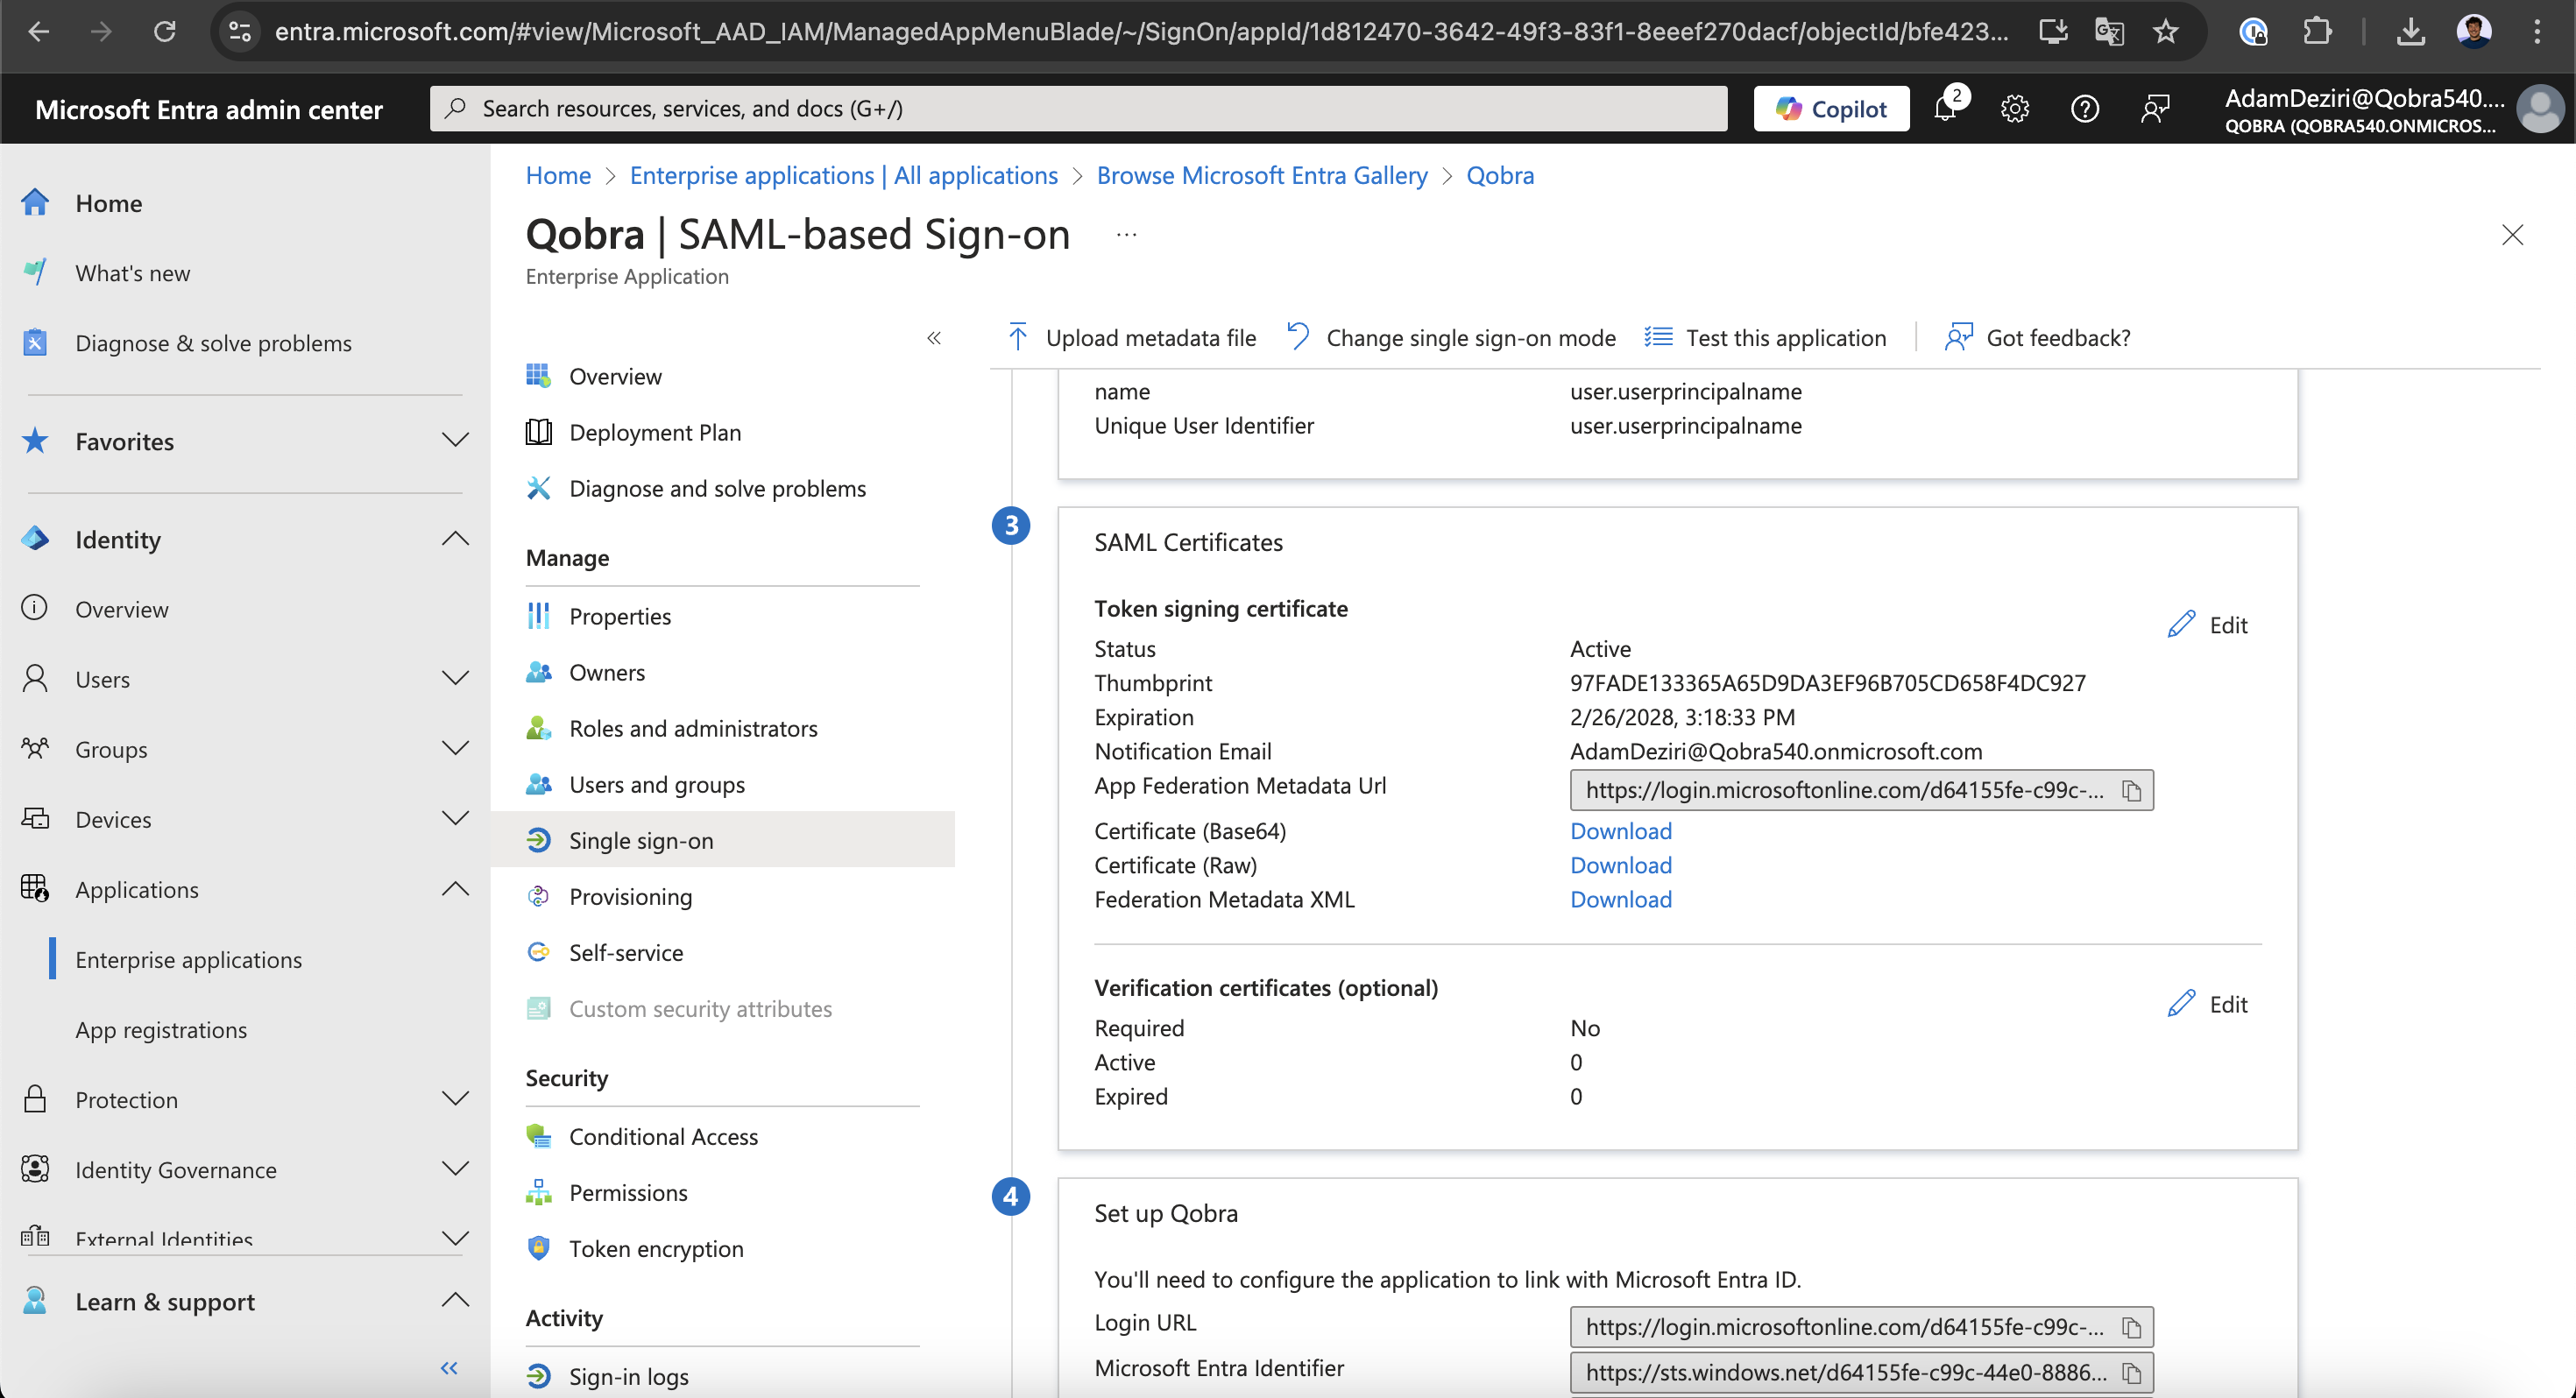
In SAML Certificates, copy the App Federation Metadata Url and paste it in the Qobra Metadata URL field.
- In Users and groups, assign the people or groups who sign in to Qobra.
Keycloak
Keycloak
-
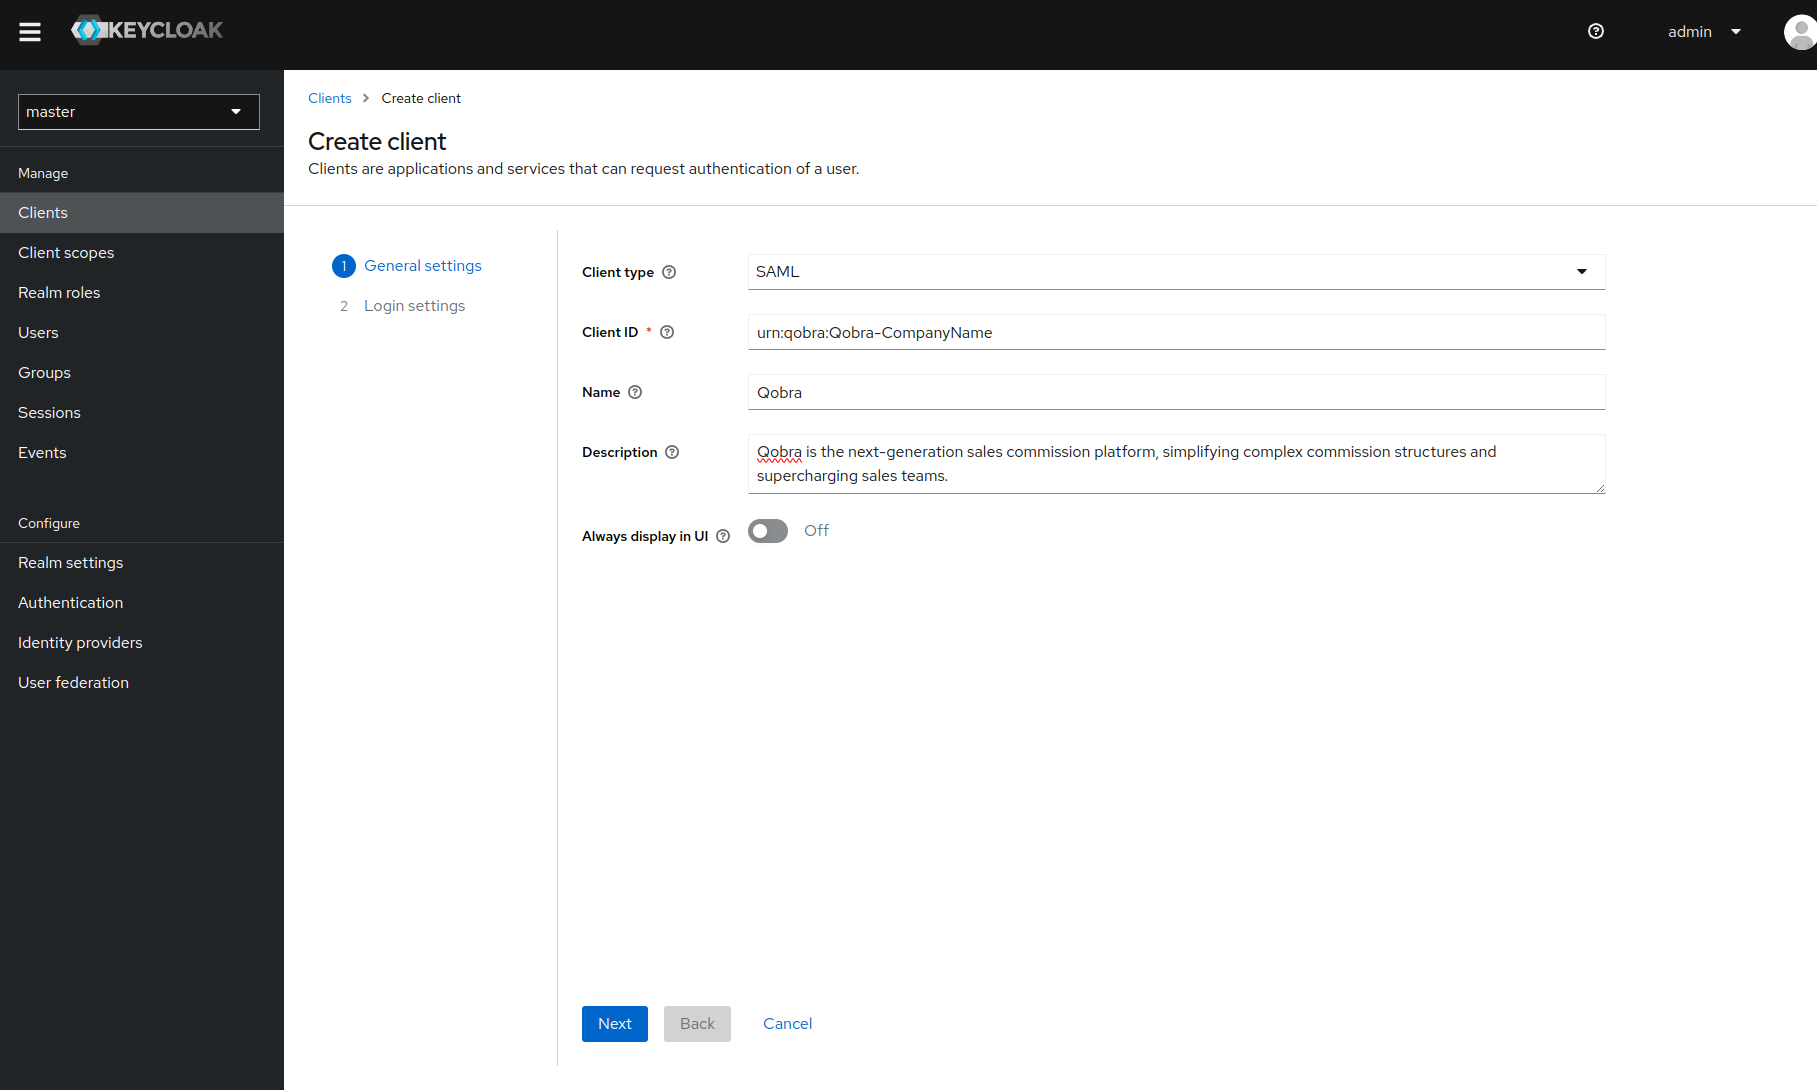
In the administration console, add a client of type SAML.
-
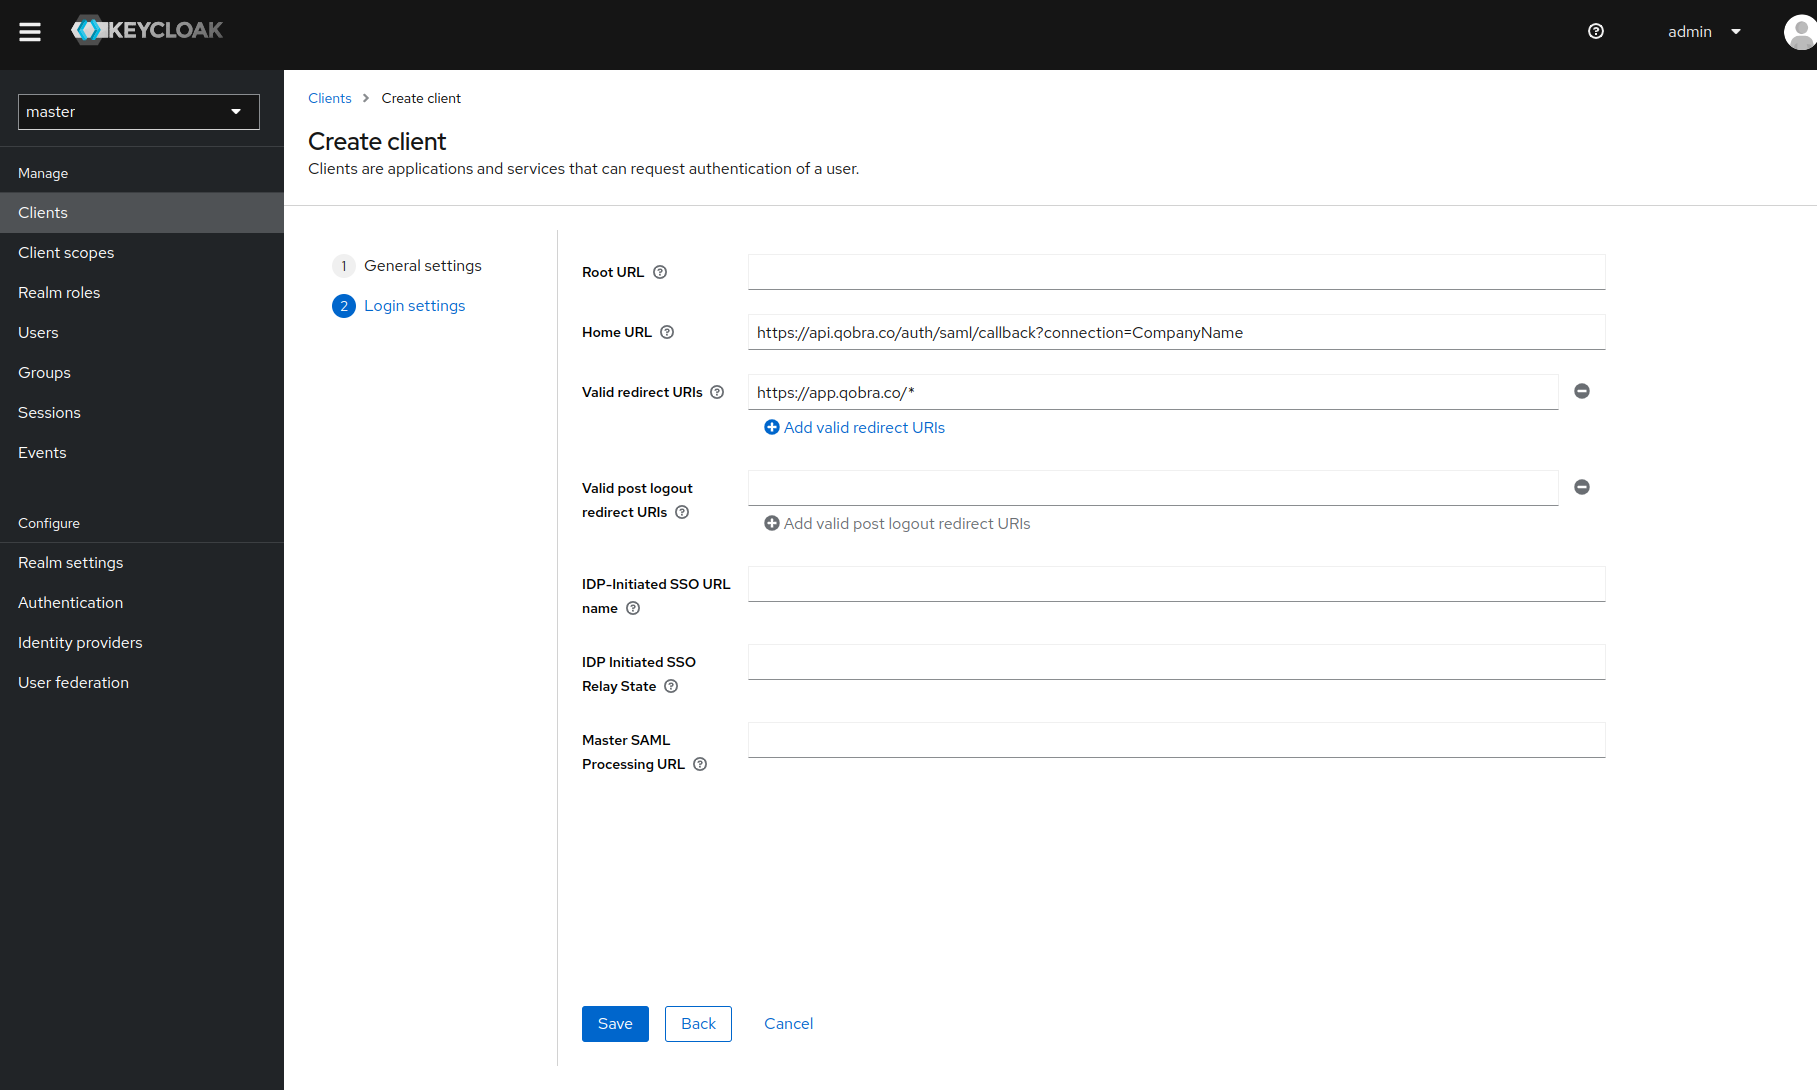
Go to the next step and fill in the login settings as shown below.
-
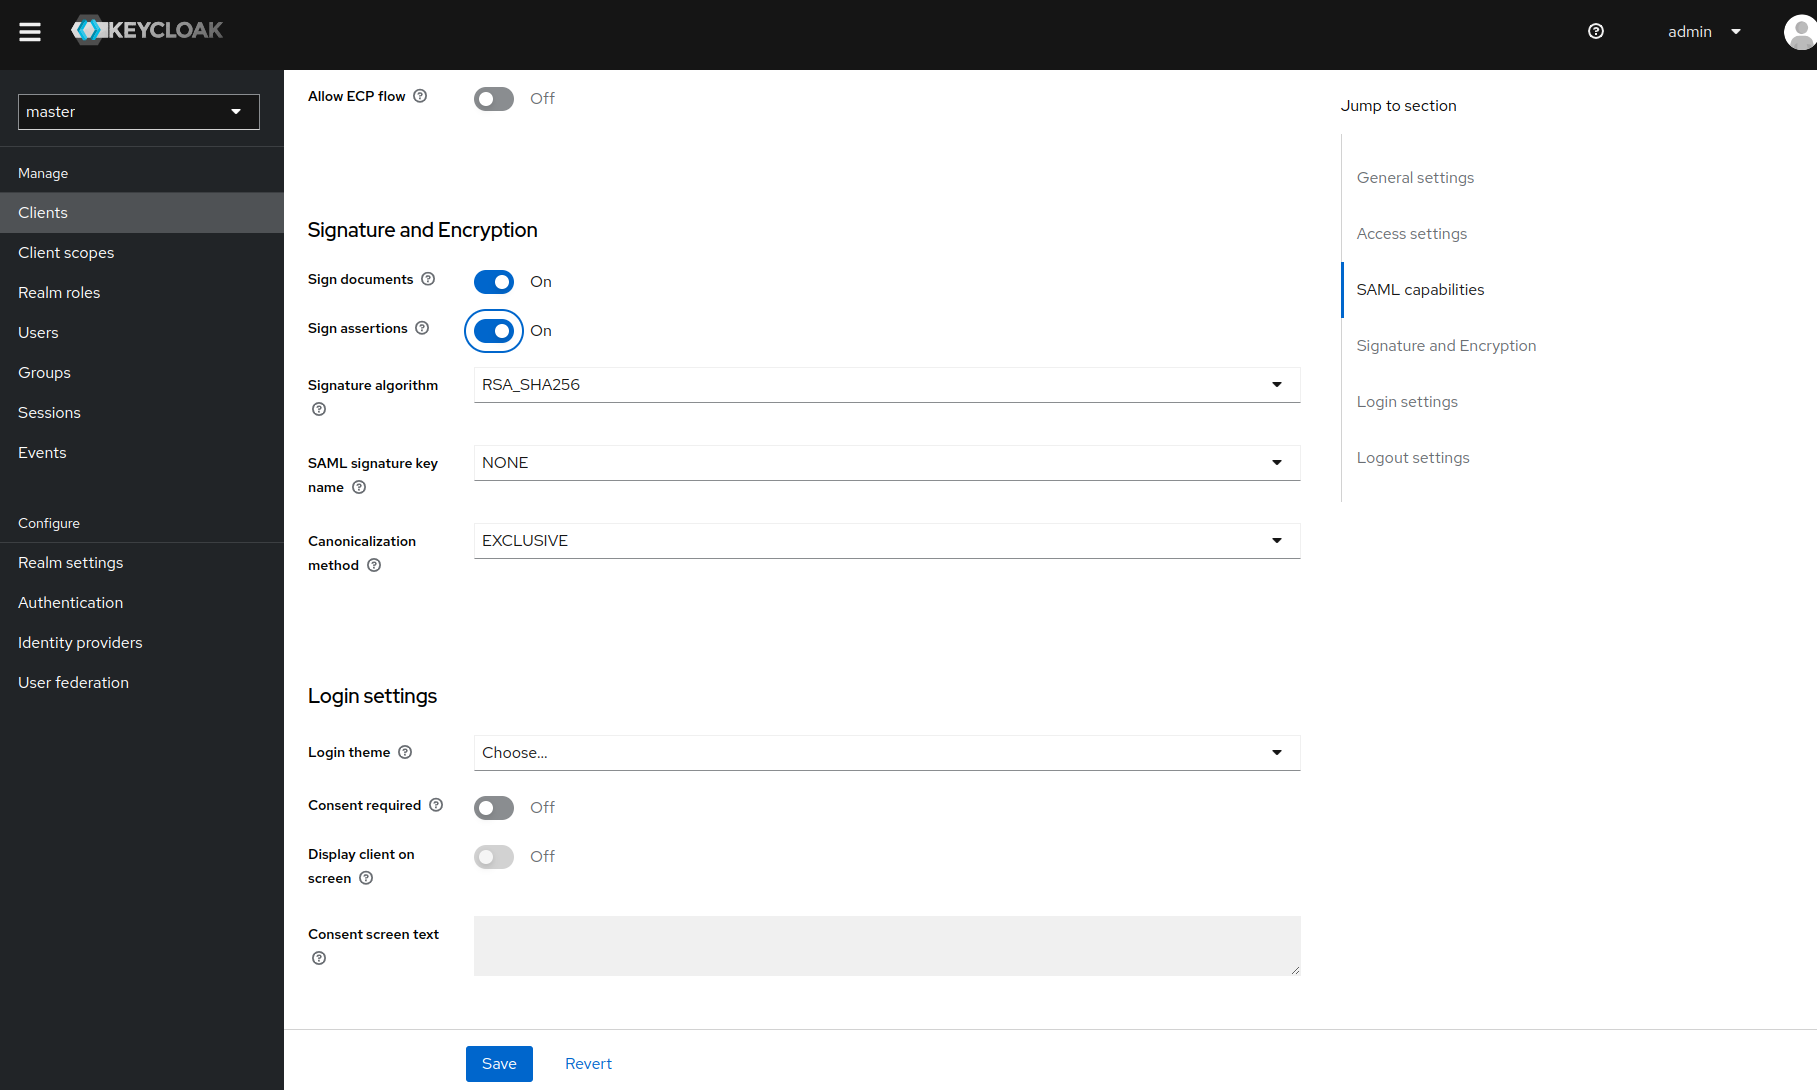
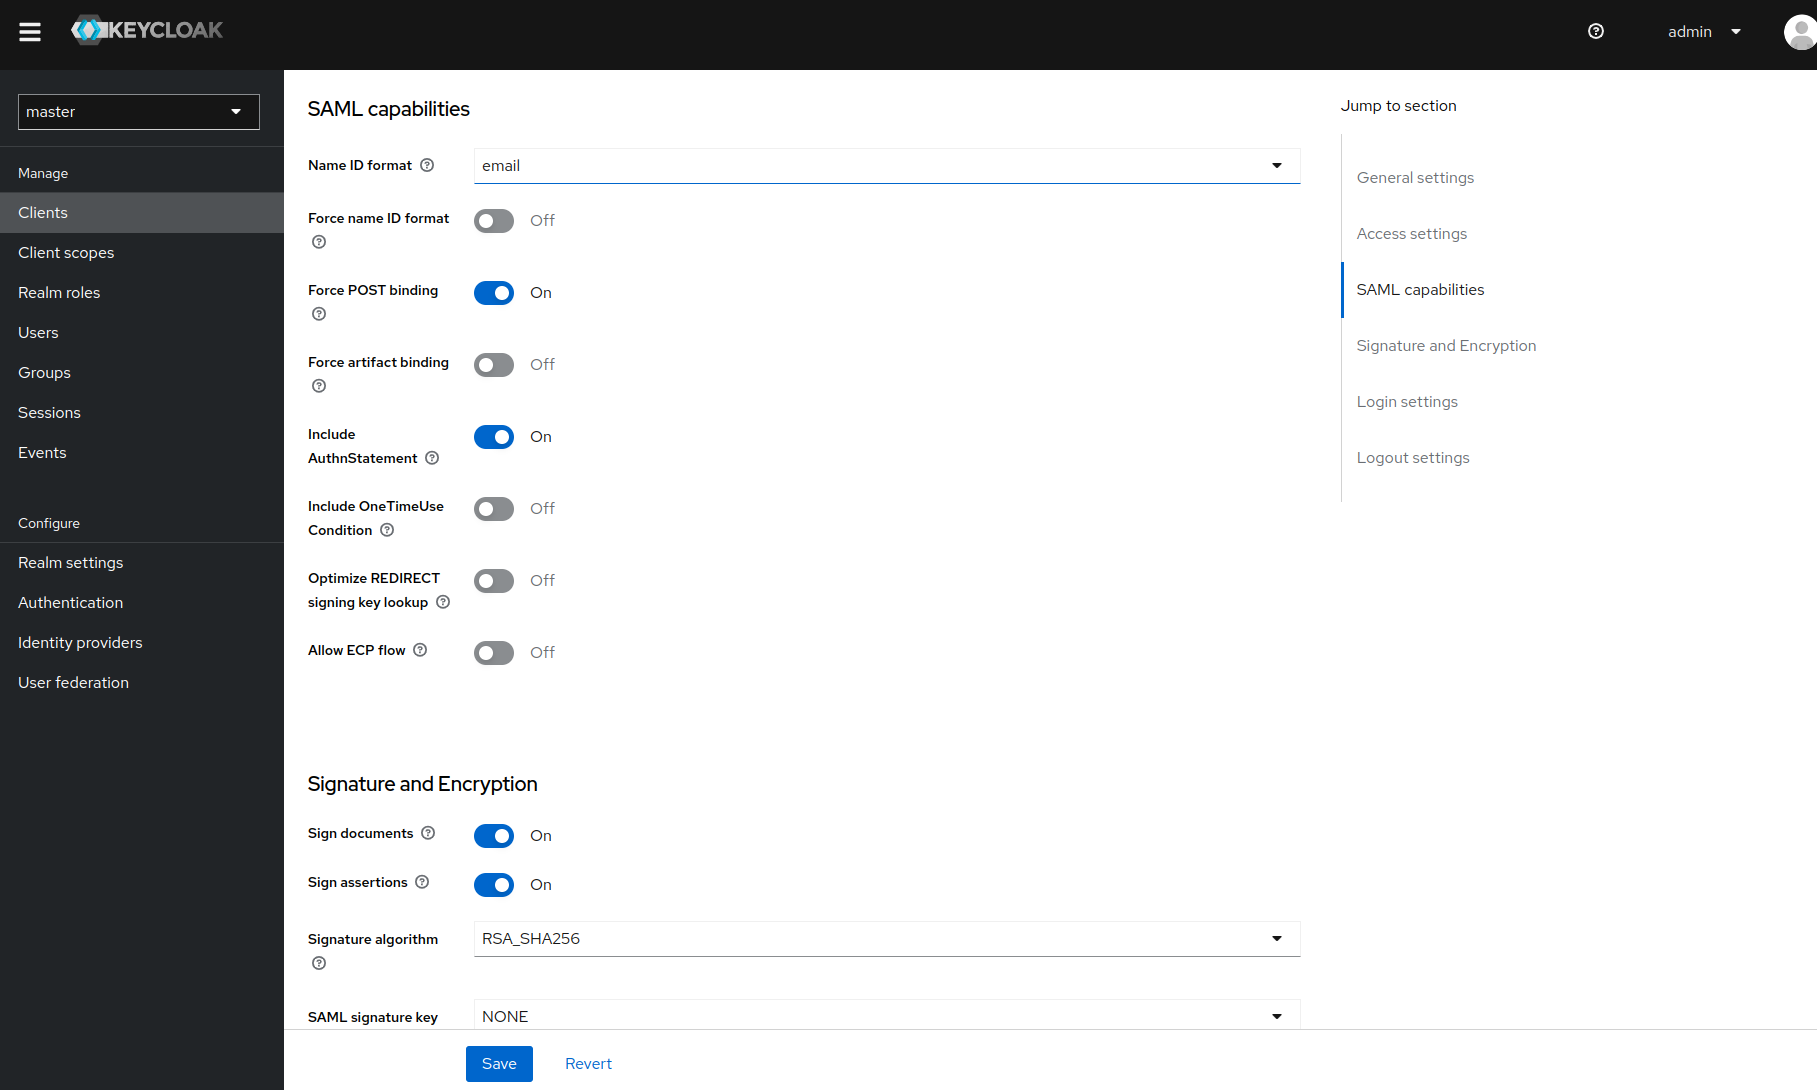
Once the client is created, set these options:
-
Sign assertions: on
-
Name ID format: email
-
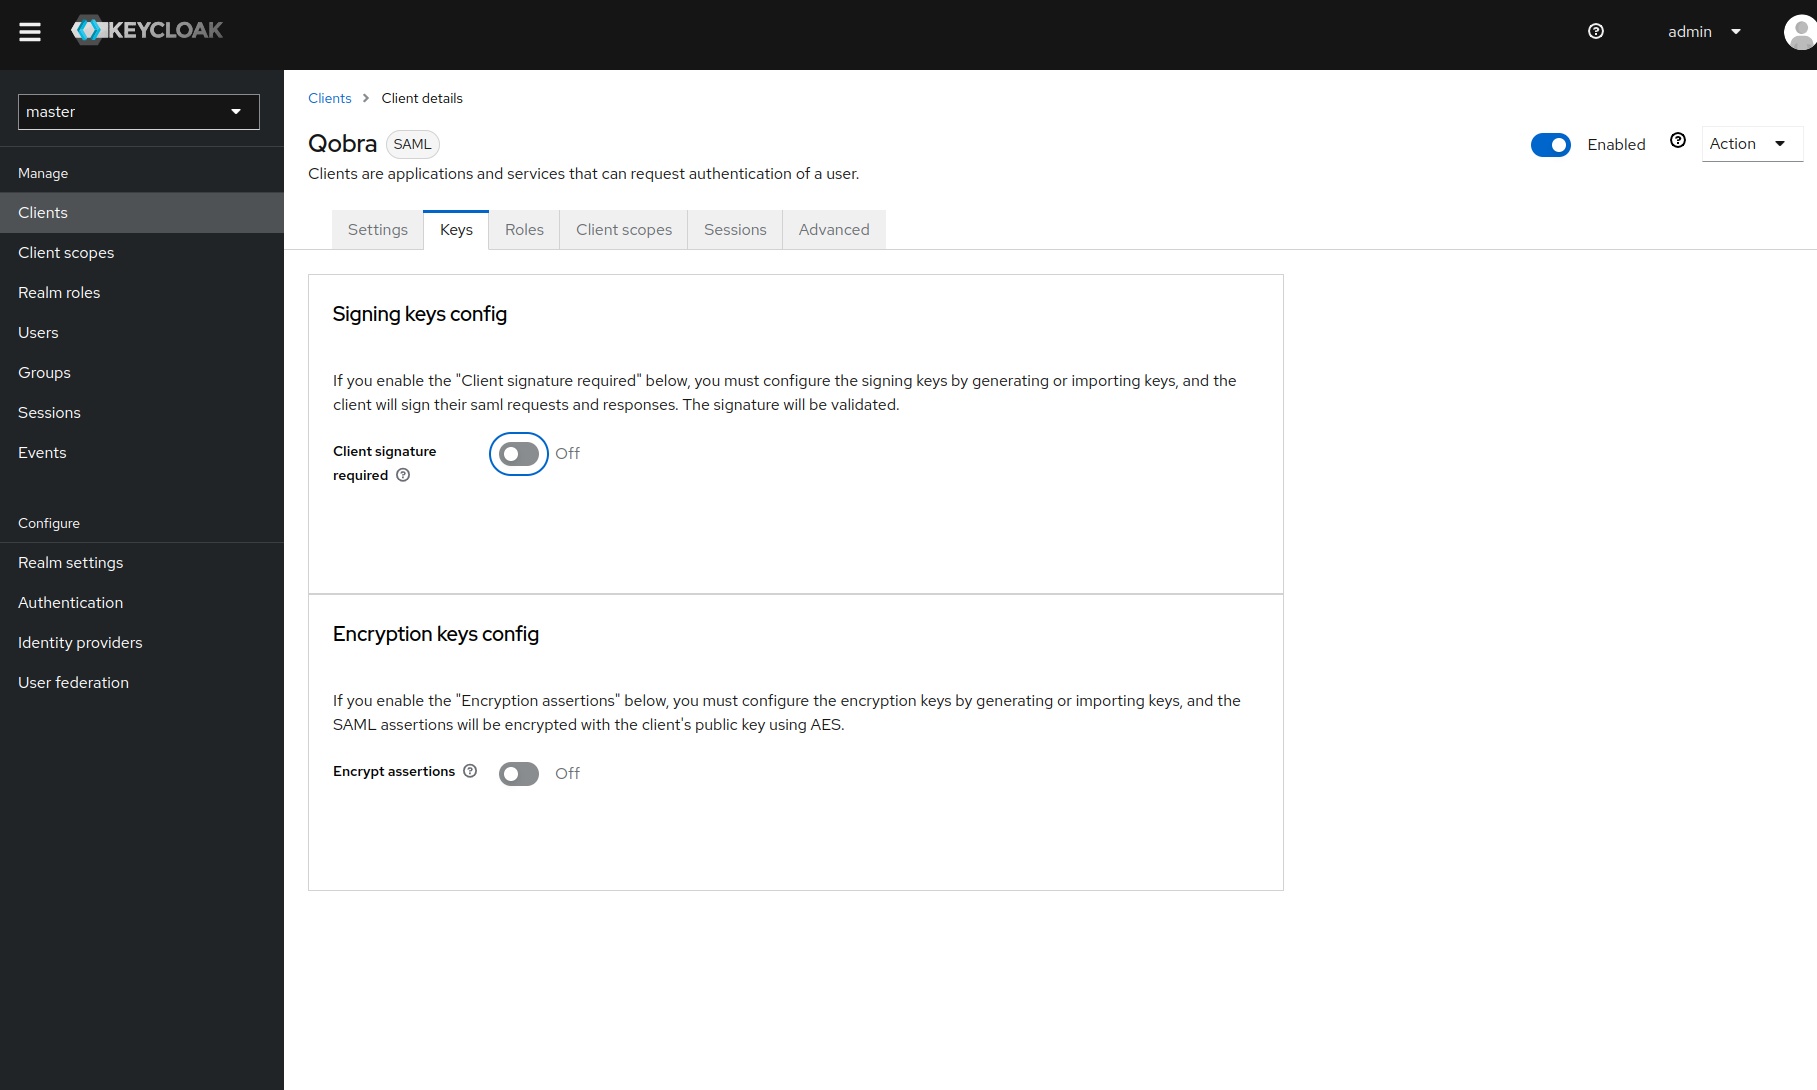
Client signature required, in the Keys tab: off
-
Sign assertions: on
-
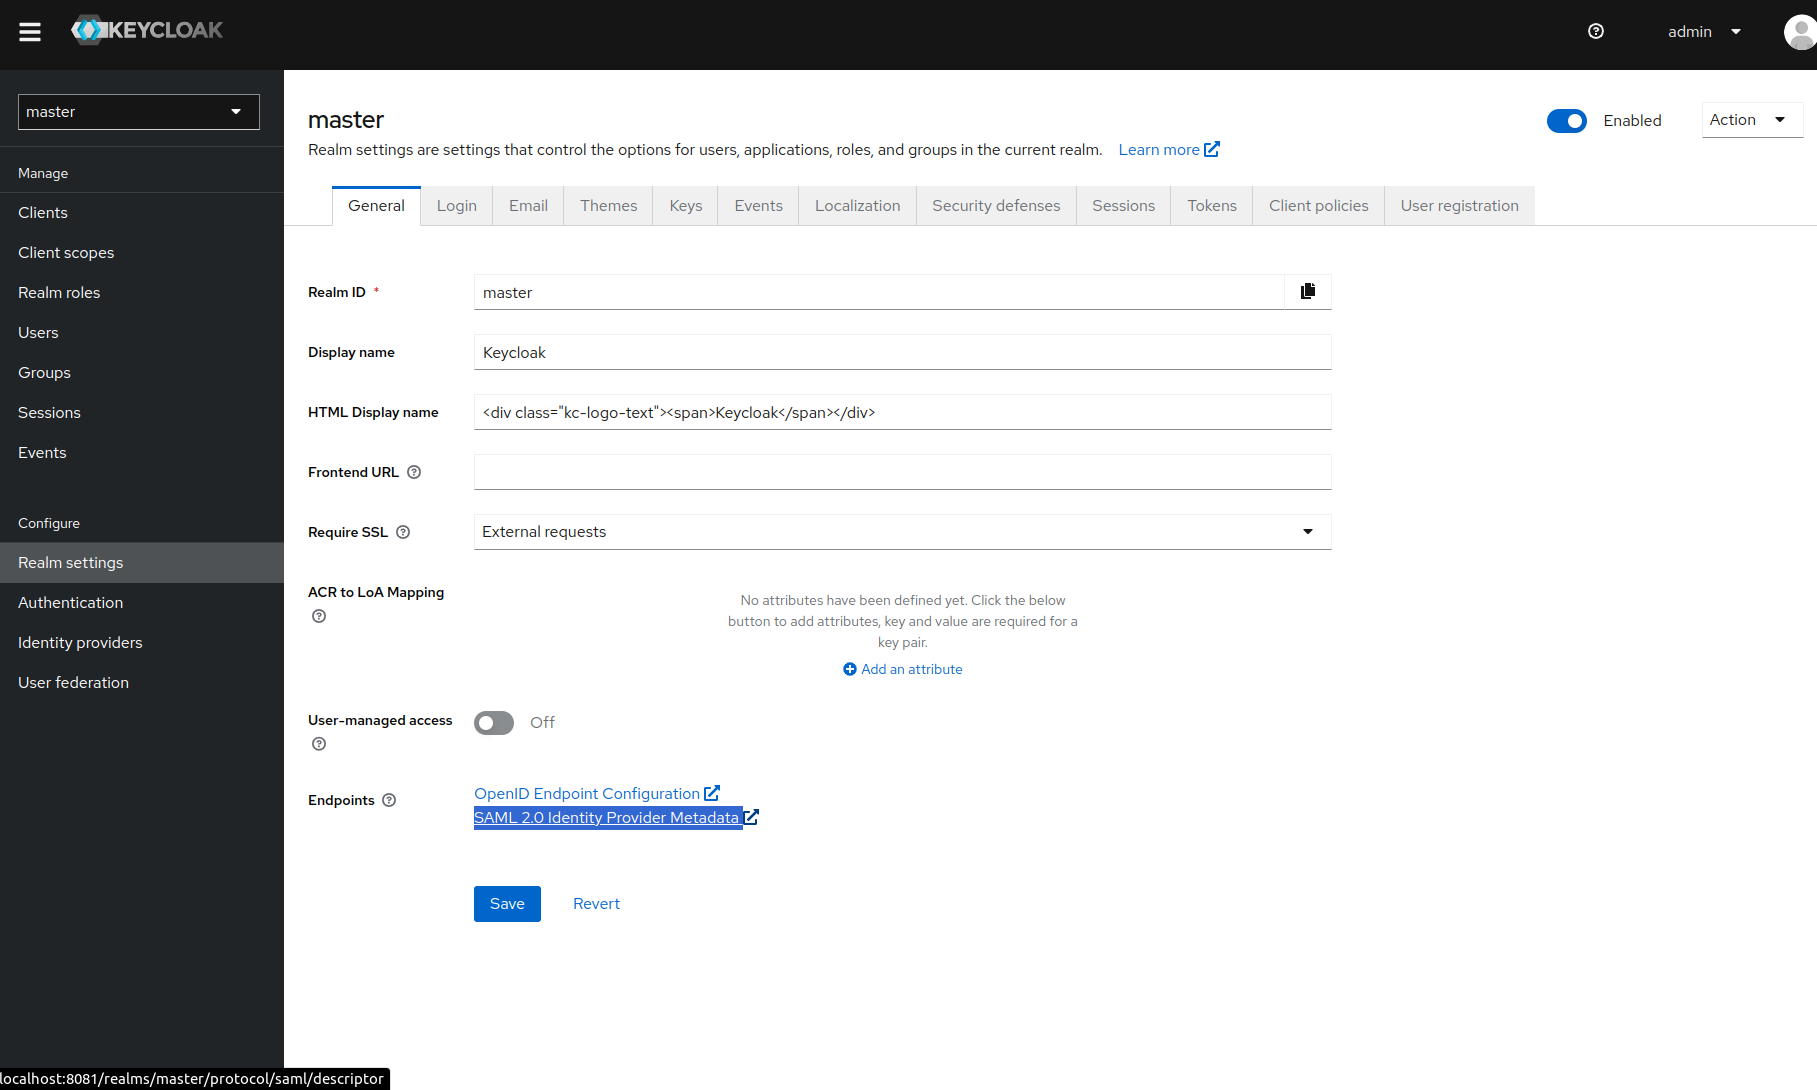
Copy the metadata URL and paste it in the Qobra Metadata URL field.
Troubleshooting
I can't find the metadata URL
I can't find the metadata URL
Okta, Microsoft Entra ID and Keycloak each give a metadata URL: see the
tutorials above. If your identity provider only lets you download the
metadata file, serve it from a public URL (cloud storage, static server):
Qobra doesn’t accept a metadata file upload.
The metadata URL is rejected
The metadata URL is rejected
Qobra must reach the URL from the internet. A URL that points to your
internal network, such as a self-hosted identity provider, is blocked for
security. Serve the metadata from a public URL.
Users can't sign in after the setup
Users can't sign in after the setup
Open the metadata URL in your browser. It must return an XML document, not
an error, and the assertions must be signed. Check that the user is
assigned to the Qobra application in your identity provider and exists in
Qobra with the same email.
I can't change the domain name
I can't change the domain name
For security, the domain name must match the domain of the admin who sets
up SSO, and public email domains such as gmail.com or outlook.com are
refused. To use another domain or add a second one, contact
support@qobra.co.